Solved LogJammer from Hack The Box!
| Field | Details |
|---|---|
| Case Reference | HTB-SHRLCK-LOGJAMMER |
| Platform | Hack The Box — Sherlock |
| Category | DFIR — Windows Event Log Analysis |
| Difficulty | — |
| Date Opened | 2025-12-03 |
| Severity | High |
| Status | Closed — training scenario |
| Host | DESKTOP-887GK2L |
| Attack Date | 2023-03-27 |
| Stack | .evtx logs (PowerShell-Operational, Security, System, Windows Defender-Operational, Windows Firewall-Firewall) |
| Tools | Chainsaw, Hayabusa, jq, Splunk |
Scenario: LogJammer — a technical assessment for a junior DFIR consultant role at Forela-Security. The user CyberJunkie logged in to his computer and may have taken malicious actions. Analyze the given event logs and report back.
1. Executive Summary
On 2023-03-27 the user CyberJunkie on DESKTOP-887GK2L logged in at 14:37:09 UTC and performed a series of malicious actions over ~25 minutes: downloaded SharpHound (quarantined by Defender), added a Windows Firewall rule “Metasploit C2 Bypass” (outbound port 4444), changed the audit policy to disable success auditing for Object Access Events, created a scheduled task \HTB-AUTOMATION (running Automation-HTB.ps1 with an email argument), computed the MD5 hash of the script, and cleared the Firewall event log to remove evidence. The entire chain was reconstructed by correlating Security, Firewall, Defender, PowerShell and System event logs.
1.1 Incident Summary
| Field | Details |
|---|---|
| Incident Type | Defense evasion + persistence via scheduled task |
| Initial Access | Valid account CyberJunkie |
| Discovery | Blue team event log analysis |
| First Execution | 2023-03-27 14:37:09 UTC (successful logon) |
| Persistence | Scheduled task \HTB-AUTOMATION → Automation-HTB.ps1 |
| Overall Severity | High |
1.2 Key Findings
CyberJunkielogged in at 14:37:09 UTC (two near-simultaneous 4624 events — Kerberos + NTLM).- SharpHound-v1.1.0.zip downloaded from GitHub and quarantined by Defender at 14:42:34 UTC.
- Firewall rule “Metasploit C2 Bypass” added — outbound port 4444 (Metasploit default) — at 14:44:43 UTC.
- Audit policy changed at 14:50:03 UTC: success auditing disabled for “Other Object Access Events”.
- Scheduled task
\HTB-AUTOMATIONcreated at 14:51:21 UTC, runningAutomation-HTB.ps1 -A cyberjunkie@hackthebox.eu. Get-FileHash -Algorithm md5executed onAutomation-HTB.ps1at 14:58:33 UTC.- Firewall event log cleared at 15:01:56 UTC (EventID 104) by
CyberJunkie.
2. Investigation Scope & Artifacts
2.1 Artifacts Analyzed
| Artifact | Format | What it answers |
|---|---|---|
all_logs.json |
JSON (Chainsaw dump of all EVTX) | All questions Q1–Q12 |
logjammer.json |
Hayabusa JSON timeline | Rule titles (Defender alert, log cleared) |
chainsaw_dump.json |
JSON (exported EVTX) | Splunk queries (Q11) |
2.2 Tools & Methods
| Tool | Purpose |
|---|---|
| Chainsaw | Dump EVTX to JSON (chainsaw dump … -j -o all_logs.json --skip-errors) |
| Hayabusa | JSON timeline generation (hayabusa json-timeline -d … -U -o logjammer.json) |
| jq | Parse and filter JSON log output |
| Splunk | Query and correlate PowerShell and Hayabusa logs |
2.3 Event ID Reference
| Source | ID | Description |
|---|---|---|
| Windows Security | 4624 |
Successful logon |
| Windows Security | 4625 |
Failed logon |
| Windows Security | 4698 |
Scheduled task created |
| Windows Security | 4719 |
System audit policy changed |
| Windows Firewall | 2004 |
Firewall rule added |
| Windows System | 104 |
Log file cleared (with log name) |
| Windows System | 102 |
Log clearing occurred (no details) |
| Windows Defender | 1116 |
Threat detected |
| PowerShell | 4104 |
Script Block Logging |
3. Technical Analysis
3.1 Scenario
Windows event log analysis of a malicious session on DESKTOP-887GK2L. The user CyberJunkie logged in and performed a series of malicious actions over ~25 minutes: firewall tampering, audit policy change, scheduled-task persistence, SharpHound download (quarantined), hash computation, and targeted log clearing.
3.2 Q1 — When did the cyberjunkie user first successfully log into his computer? (UTC)
Answer: 2023-03-27 14:37:09
cat all_logs.json | jq '. [] | select(.Event.System.EventID == 4624 and .Event.EventData.TargetUserName == "CyberJunkie") | " \(.Event.EventData.TargetUserName) connect to \(.Event.System.TimeCreated_attributes.SystemTime)"'
Output:
" CyberJunkie connect to  2023-03-27T14:37:09.879891Z"
" CyberJunkie connect to  2023-03-27T14:37:09.879940Z"
" CyberJunkie connect to  2023-03-27T14:38:32.937423Z"
" CyberJunkie connect to  2023-03-27T14:38:32.937458Z"
Notes: EventID 4624 = Successful logon, filtered by TargetUserName CyberJunkie. Two duplicate timestamps at 14:37:09 (879891Z and 879940Z) are normal — Windows logs one event for Kerberos and one for NTLM authentication simultaneously. The first timestamp is the answer: 2023-03-27 14:37:09 UTC.
MITRE ATT&CK: T1078 — Valid Accounts (Initial Access).
Detection angle. EID 4624 filtered by TargetUserName — first successful logon timestamp; duplicate Kerberos/NTLM events are normal.
3.3 Q2 — The user tampered with firewall settings. What is the Name of the firewall rule added?
Answer: Metasploit C2 Bypass
Step 1 — List all firewall rule names:
cat all_logs.json | jq '.[] | select(.Event.System.Channel=="Microsoft-Windows-Windows Firewall With Advanced Security/Firewall") | .Event.EventData.RuleName' | sort | uniq -c | sort -hr
Output:
1 "Network Discovery (NB-Datagram-In)"
1 "Metasploit C2 Bypass"
1 "Cloud Identity (TCP-Out)"
Step 2 — Get full details of the suspicious rule:
cat all_logs.json | jq '.[] | select(.Event.System.Channel=="Microsoft-Windows-Windows Firewall With Advanced Security/Firewall" and .Event.EventData.RuleName == "Metasploit C2 Bypass")'
Key fields:
{
  "EventID": 2004,
  "SystemTime": "2023-03-27T14:44:43.415702Z",
  "RuleName": "Metasploit C2 Bypass",
  "Direction": 2,
  "Protocol": 6,
  "RemotePorts": "4444",
  "Action": 3,
  "Active": 1,
  "ModifyingApplication": "C:\\Windows\\System32\\mmc.exe",
  "ModifyingUser": "S-1-5-21-3393683511-3463148672-371912004-1001"
}
Notes: EventID 2004 = Windows Firewall rule added. The rule name “Metasploit C2 Bypass” immediately stands out — Metasploit is the most widely used exploitation framework. Key fields: RemotePorts 4444 (Metasploit default reverse shell port), Direction 2 (Outbound), Action 3 (Allow), ModifyingApplication mmc.exe. Timestamp 14:44:43 UTC — 7 minutes after initial login.
MITRE ATT&CK: T1562.004 (Impair Defenses: Disable or Modify System Firewall), T1571 (Non-Standard Port).
Detection angle. EID 2004 with RuleName containing “Metasploit” or RemotePorts 4444 — firewall rule allowing Metasploit C2.
3.4 Q3 — What’s the direction of the firewall rule?
Answer: outbound
Identified from the same EventID 2004 event in Q2. Direction field mapping: 1 = Inbound, 2 = Outbound (this rule). Direction 2 = Outbound means the victim machine initiates the connection TO the attacker’s C2 server on port 4444 — a classic reverse shell pattern (Metasploit’s meterpreter or shell/reverse_tcp).
MITRE ATT&CK: T1071 (Application Layer Protocol).
Detection angle. EID 2004 Direction=2 (outbound) to port 4444 — reverse shell firewall allowance.
3.5 Q4 — The user changed audit policy of the computer. What’s the Subcategory of this changed policy?
Answer: Other Object Access Events
cat all_logs.json | jq '.[] | select(.Event.System.EventID == 4719)'
Key fields:
{
  "EventID": 4719,
  "SystemTime": "2023-03-27T14:50:03.721835Z",
  "SubjectUserName": "DESKTOP-887GK2L$",
  "SubjectLogonId": "0x3e7",
  "CategoryId": "%%8274",
  "SubcategoryId": "%%12804",
  "SubcategoryGuid": "0CCE9227-69AE-11D9-BED3-505054503030",
  "AuditPolicyChanges": "%%8449"
}

Notes: EventID 4719 = System Audit Policy Changed. The subcategory is identified by SubcategoryGuid, not the %% codes (which can be misleading): 0CCE9227-69AE-11D9-BED3-505054503030 → “Other Object Access Events”. AuditPolicyChanges %%8449 = Success auditing removed. The attacker disabled success auditing for Object Access Events, blinding the SIEM to successful file/object access operations. This occurred at 14:50:03 — 6 minutes after the firewall rule was added — confirming systematic defense evasion.
MITRE ATT&CK: T1562.002 (Impair Defenses: Disable Windows Event Logging).
Detection angle. EID 4719 with SubcategoryGuid 0CCE9227-… and AuditPolicyChanges %%8449 — disabling success auditing for Object Access.
3.6 Q5 — The user “cyberjunkie” created a scheduled task. What’s the name of this task?
Answer: \\HTB-AUTOMATION
cat all_logs.json | jq '.[] | select(.Event.System.EventID == 4698)'
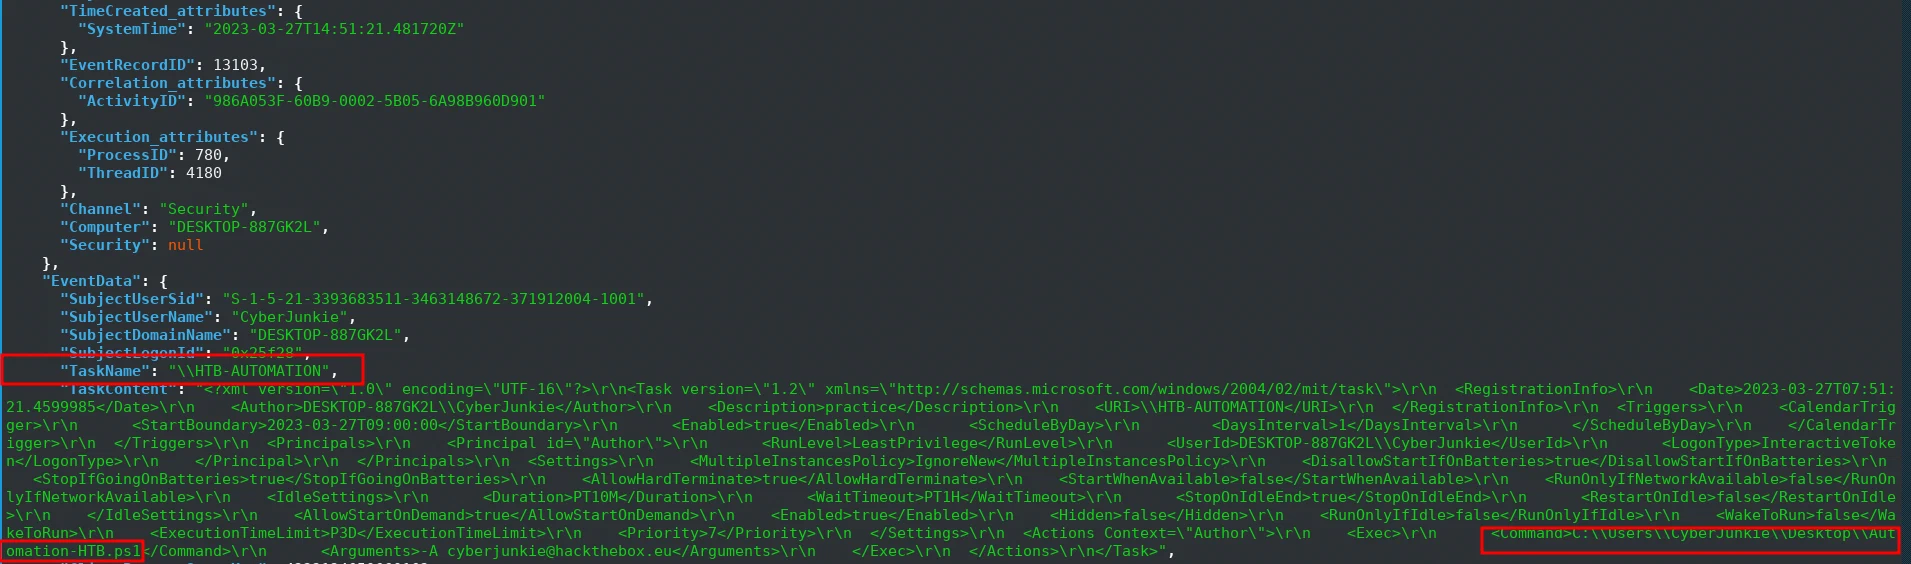
Notes: EventID 4698 = Scheduled Task Created, logged in Security.evtx. Task created at 2023-03-27 14:51:21 UTC by CyberJunkie. TaskName: \\HTB-AUTOMATION. The TaskContent XML contains the full command and arguments. SubjectUserSid confirms this was created by the CyberJunkie account.
MITRE ATT&CK: T1053.005 (Scheduled Task/Job: Scheduled Task), T1053 (Scheduled Task/Job).
Detection angle. EID 4698 — scheduled task creation by a non-system account.
3.7 Q6 — What’s the full path of the file which was scheduled for the task?
Answer: C:\Users\CyberJunkie\Desktop\Automation-HTB.ps1
Extracted from the TaskContent XML field in the same EventID 4698 event from Q5. The TaskContent contains the full XML definition of the scheduled task including the command to execute: C:\Users\CyberJunkie\Desktop\Automation-HTB.ps1. The file is a PowerShell script located on the user’s Desktop — not hidden in AppData or system directories.
Detection angle. EID 4698 TaskContent XML → <Command> field reveals the scheduled executable path.
3.8 Q7 — What are the arguments of the command?
Answer: -A cyberjunkie@hackthebox.eu
Extracted from the TaskContent XML field in EventID 4698 (Q5). Full command: C:\Users\CyberJunkie\Desktop\Automation-HTB.ps1 -A cyberjunkie@hackthebox.eu. The -A flag with an email address suggests the script accepts an email parameter — likely for sending results or notifications. Combined with the GetFileHash command (Q11), the attacker likely computed a hash of the script and emailed the result — a simple data exfiltration or integrity verification mechanism.
MITRE ATT&CK: T1048 (Exfiltration Over Alternative Protocol).
Detection angle. EID 4698 TaskContent XML → <Arguments> field reveals command-line arguments.
3.9 Q8 — The antivirus running on the system identified a threat and performed actions on it. Which tool was identified as malware by antivirus?
Answer: SharpHound
cat logjammer.json | jq 'select(.RuleTitle == "Defender Alert (High)")'
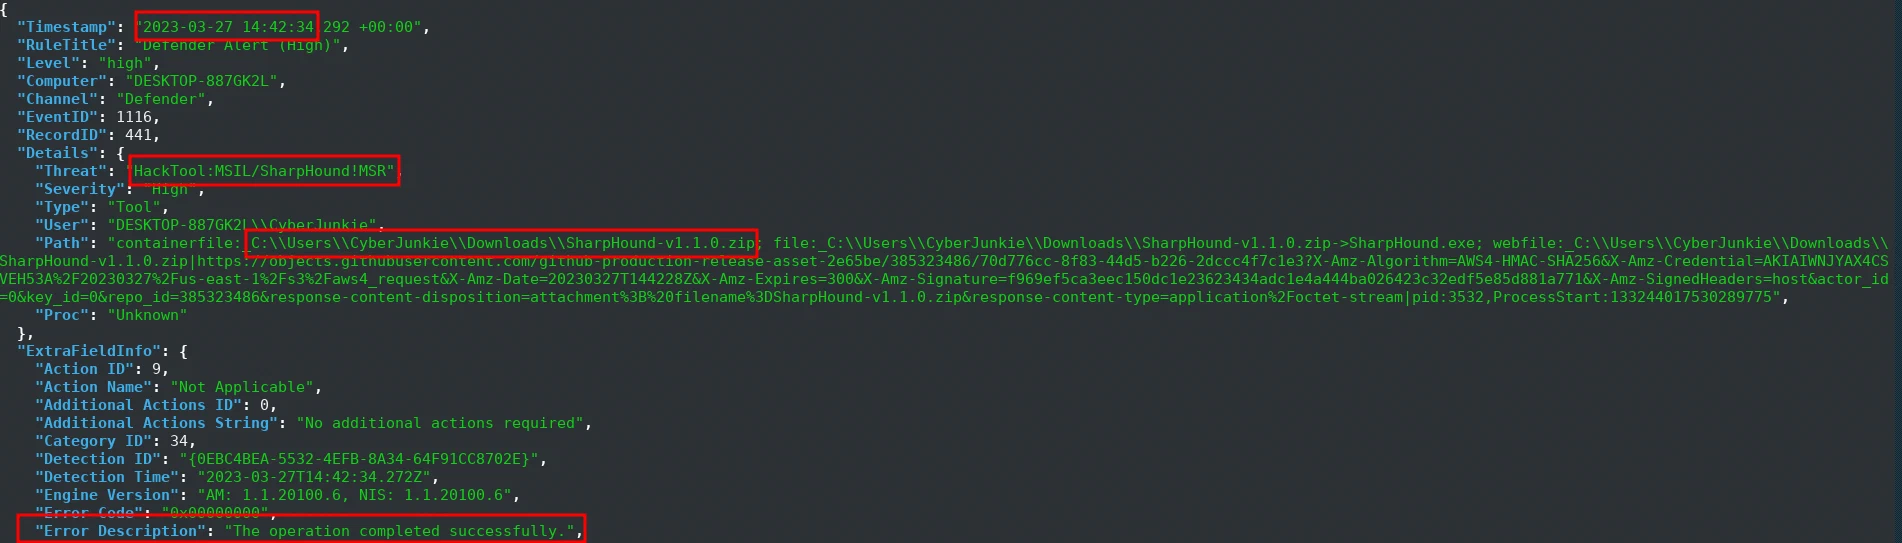
Notes: Defender EventID 1116 = Threat detected. Two simultaneous detections at 14:42:34 UTC:
- HackTool:PowerShell/SharpHound.B → SharpHound.ps1
- HackTool:MSIL/SharpHound!MSR → SharpHound.exe
Both detected inside SharpHound-v1.1.0.zip downloaded directly from GitHub (Origin: Internet, Source: Downloads and attachments). SharpHound is the data collector component of BloodHound — an Active Directory attack path analysis tool. It enumerates all users, groups, computers, GPOs, ACLs, session data, and trust relationships. The collected data is fed into BloodHound to visualise attack paths from any user to Domain Admin — indicating the attacker was planning full Active Directory compromise.
MITRE ATT&CK: T1069.002 (Permission Groups Discovery: Domain Groups), T1087.002 (Account Discovery: Domain Account), T1005 (Data from Local System).
Detection angle. Hayabusa Defender Alert (High) rule on EID 1116 — Defender threat detection for SharpHound.
3.10 Q9 — What’s the full path of the malware which raised the alert?
Answer: C:\Users\CyberJunkie\Downloads\SharpHound-v1.1.0.zip
Extracted from the Path field of Defender EventID 1116 in Q8. Full path from the event: containerfile: C:\Users\CyberJunkie\Downloads\SharpHound-v1.1.0.zip. The “containerfile:” prefix indicates Defender detected the threat inside a ZIP archive before extraction. The file was downloaded directly to the Downloads folder from https://objects.githubusercontent.com/github-production-release-asset-2e65be/385323486/… — the official BloodHound GitHub release. The attacker downloaded the tool directly from its public repository rather than using a custom or obfuscated version.
Detection angle. Defender EID 1116 Path field with containerfile: prefix — threat inside a ZIP archive.
3.11 Q10 — What action was taken by the antivirus?
Answer: Quarantine
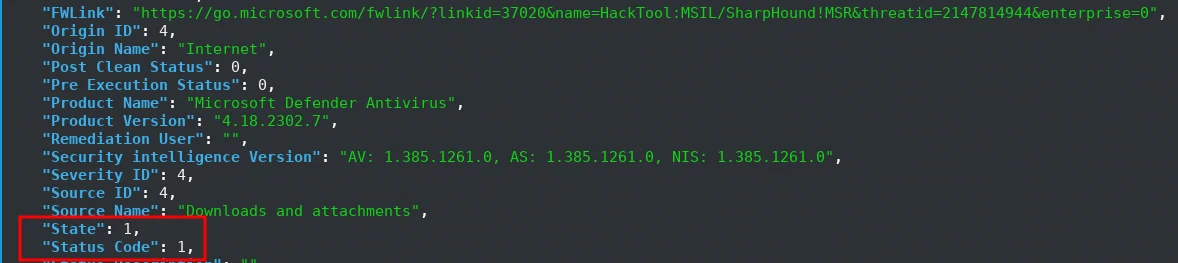
Notes: Identified from the State field in Defender EventID 1116 (Q8). Windows Defender State field mapping: 0 = Unknown, 1 = Quarantined (this event), 2 = Removed, 3 = Allowed, 4 = No Action. State: 1 = Quarantined — Defender successfully quarantined SharpHound before it could be executed. Important distinction: Action ID 9 = “Not Applicable” refers to the remediation action TYPE, not the outcome. The actual result is always in the State field. Both SharpHound.ps1 and SharpHound.exe were quarantined simultaneously at 14:42:34 UTC inside the ZIP archive.
Detection angle. Defender EID 1116 State field = 1 (Quarantined) — threat contained before execution.
3.12 Q11 — The user used PowerShell to execute commands. What command was executed by the user?
Answer: Get-FileHash -Algorithm md5 .\Desktop\Automation-HTB.ps1
Splunk query:
source="all_logs.json" host="parrot" sourcetype="_json" "Event.System.Channel"="Microsoft-Windows-PowerShell/Operational"
| spath input=_raw output=Timestamp path="Event.System.TimeCreated_attributes.SystemTime"
| spath input=_raw output=EventID path="Event.System.EventID"
| spath input=_raw output=Command path="Event.EventData.ScriptBlockText"
| where Timestamp>"2023-03-27 14:37*"
| search "Event.System.EventID"=4104
| table Timestamp, EventID, Command

Notes: Splunk used here instead of jq because PowerShell Script Block Logging (EventID 4104) generates many events and Splunk’s tabular output makes it easier to read ScriptBlockText. Filtered by Channel Microsoft-Windows-PowerShell/Operational, EventID 4104, Timestamp after initial login at 14:37. Two commands found: 1. “prompt” (benign), 2. Get-FileHash -Algorithm md5 .\Desktop\Automation-HTB.ps1. Get-FileHash computes the MD5 hash of the scheduled task script. Combined with the email argument in Q7, the attacker likely computed the hash and emailed it — either as verification or as simple data exfiltration. Executed at 2023-03-27 14:58:33 UTC.
MITRE ATT&CK: T1059.001 (Command & Scripting Interpreter: PowerShell), T1074 (Data Staged).
Detection angle. EID 4104 ScriptBlockText containing Get-FileHash on a scheduled-task script — hash computation for verification/exfiltration.
3.13 Q12 — We suspect the user deleted some event logs. Which Event log file was cleared?
Answer: Microsoft-Windows-Windows Firewall With Advanced Security/Firewall
Splunk Query 1 (check all RuleTitles):
source="logjammer.json" host="parrot" sourcetype="_json" | stats count by RuleTitle

Splunk Query 2:
source="logjammer.json" host="parrot" sourcetype="_json" RuleTitle="Log File Cleared"
Result:
{
    "Timestamp": "2023-03-27 15:01:56.515 +00:00",
    "RuleTitle": "Log File Cleared",
    "Level": "med",
    "Computer": "DESKTOP-887GK2L",
    "Channel": "Sys",
    "EventID": 104,
    "RecordID": 2186,
    "Details": {
        "Log": "Microsoft-Windows-Windows Firewall With Advanced Security/Firewall",
        "User": "CyberJunkie"
    },
    "ExtraFieldInfo": {
        "BackupPath": "",
        "SubjectDomainName": "DESKTOP-887GK2L"
    }
}
Notes: Two relevant EventIDs for log clearing: EventID 102 = Log clearing occurred (no details on which log); EventID 104 = Log file cleared WITH the specific log name. Used EventID 104 which provides the Log field containing the exact log file cleared. The attacker specifically cleared the Firewall log at 15:01:56 — the same log that contained evidence of the “Metasploit C2 Bypass” rule addition (14:44:43). This is targeted, deliberate log clearing to remove specific evidence of firewall tampering, not a blanket wipe of all logs.
MITRE ATT&CK: T1070.001 (Indicator Removal: Clear Windows Event Logs).
Detection angle. EID 104 (not 102) provides the specific log name cleared — targeted anti-forensics.
4. Challenge Q&A Log
| # | Question | Answer | Method |
|---|---|---|---|
| 1 | First successful logon time | 2023-03-27 14:37:09 |
EID 4624 (CyberJunkie) |
| 2 | Firewall rule name added | Metasploit C2 Bypass |
EID 2004 (Firewall) |
| 3 | Firewall rule direction | outbound |
EID 2004 Direction=2 |
| 4 | Audit policy subcategory changed | Other Object Access Events |
EID 4719 SubcategoryGuid |
| 5 | Scheduled task name | \\HTB-AUTOMATION |
EID 4698 |
| 6 | Scheduled task file path | C:\Users\CyberJunkie\Desktop\Automation-HTB.ps1 |
EID 4698 TaskContent |
| 7 | Command arguments | -A cyberjunkie@hackthebox.eu |
EID 4698 TaskContent |
| 8 | Malware tool identified by AV | SharpHound |
Hayabusa Defender Alert (High) |
| 9 | Full path of quarantined malware | C:\Users\CyberJunkie\Downloads\SharpHound-v1.1.0.zip |
Defender EID 1116 Path |
| 10 | Antivirus action taken | Quarantine |
Defender EID 1116 State=1 |
| 11 | PowerShell command executed | Get-FileHash -Algorithm md5 .\Desktop\Automation-HTB.ps1 |
EID 4104 ScriptBlockText |
| 12 | Event log file cleared | Microsoft-Windows-Windows Firewall With Advanced Security/Firewall |
EID 104 |
5. Incident Narrative
On 2023-03-27 the user CyberJunkie on DESKTOP-887GK2L logged in at 14:37:09 UTC and performed a series of malicious actions over ~25 minutes. After logging in, the user downloaded SharpHound (quarantined by Defender at 14:42:34). Despite this, the attacker proceeded to add a Windows Firewall rule “Metasploit C2 Bypass” to allow outbound traffic on port 4444 (14:44:43), then disabled audit logging for Object Access Events (14:50:03) to reduce visibility. A persistence mechanism was established via a scheduled task \HTB-AUTOMATION running Automation-HTB.ps1 with an email argument (14:51:21). The attacker computed the MD5 hash of the script (14:58:33), likely to verify or exfiltrate it. In a final anti-forensics step, the attacker cleared the Firewall event log (15:01:56) to remove evidence of the malicious rule. The entire attack chain was reconstructed through correlation of Security, Firewall, Defender, PowerShell and System event logs.
6. Attack Timeline
| Timestamp (UTC) | Event | Evidence |
|---|---|---|
2023-03-27 14:37:09 |
CyberJunkie successfully logged in | EID 4624 — Security.evtx |
2023-03-27 14:42:34 |
SharpHound-v1.1.0.zip downloaded and quarantined by Defender | EID 1116 — Defender log |
2023-03-27 14:44:43 |
Firewall rule “Metasploit C2 Bypass” added — port 4444 outbound | EID 2004 — Firewall log |
2023-03-27 14:50:03 |
Audit policy changed — success auditing disabled for Object Access | EID 4719 — Security.evtx |
2023-03-27 14:51:21 |
Scheduled task \HTB-AUTOMATION created |
EID 4698 — Security.evtx |
2023-03-27 14:58:33 |
PowerShell Get-FileHash executed on Automation-HTB.ps1 |
EID 4104 — PowerShell log |
2023-03-27 15:01:56 |
Firewall event log cleared to remove evidence | EID 104 — System log |
7. Indicators of Compromise (IOCs)
7.1 File IOCs
| Type | Value | Context |
|---|---|---|
| File Name | SharpHound-v1.1.0.zip |
AD enumeration tool (quarantined) — Q8/Q9 |
| File Name | Automation-HTB.ps1 |
Scheduled task payload on Desktop — Q6/Q7 |
| File Path | C:\Users\CyberJunkie\Desktop\Automation-HTB.ps1 |
Script location — Q6 |
| File Path | C:\Users\CyberJunkie\Downloads\SharpHound-v1.1.0.zip |
Download location — Q9 |
7.2 Network IOCs
| Type | Value | Context |
|---|---|---|
| Port | 4444 |
Metasploit default reverse shell port — Q2/Q3 |
| Domain | objects.githubusercontent.com |
SharpHound download source — Q9 |
7.3 Behavioral IOCs
| Type | Value | Context |
|---|---|---|
| Account | CyberJunkie |
Compromised user account |
| Host | DESKTOP-887GK2L |
Affected workstation |
| Firewall Rule | Metasploit C2 Bypass |
Outbound allow on port 4444 — Q2 |
| Scheduled Task | \HTB-AUTOMATION |
Persistence — Q5 |
| Command | Get-FileHash -Algorithm md5 .\Desktop\Automation-HTB.ps1 |
Hash computation — Q11 |
| Audit Change | Subcategory Other Object Access Events, success auditing removed |
EID 4719 — Q4 |
| Log Clearing | Firewall log cleared (EID 104) at 15:01:56 | Targeted anti-forensics — Q12 |
8. Detection Opportunities
| Source | What to look for | Why it matters |
|---|---|---|
| Windows Security (EID 4624) | Successful logon for a user account at an unusual time | Initial access — Q1 |
| Windows Firewall (EID 2004) | Rule with RemotePorts=4444 or suspicious RuleName |
Metasploit C2 allowance — Q2/Q3 |
| Windows Security (EID 4719) | Audit policy change disabling success auditing | Defense evasion — Q4 |
| Windows Security (EID 4698) | Scheduled task creation by a non-system user | Persistence — Q5 |
| Windows Defender (EID 1116) | Threat detection for SharpHound/HackTool | AD enumeration tool — Q8 |
| PowerShell (EID 4104) | Get-FileHash on a scheduled-task script |
Hash computation/exfiltration — Q11 |
| Windows System (EID 104) | Log file cleared with specific log name | Targeted anti-forensics — Q12 |
9. MITRE ATT&CK Mapping
| TTP ID | Tactic | Technique | Evidence |
|---|---|---|---|
| T1078 | Initial Access | Valid Accounts | CyberJunkie logged in — Q1 |
| T1562.004 | Defense Evasion | Impair Defenses: Disable or Modify System Firewall | “Metasploit C2 Bypass” rule, port 4444 — Q2/Q3 |
| T1571 | Command & Control | Non-Standard Port | Port 4444 outbound — Q2 |
| T1071 | Command & Control | Application Layer Protocol | Metasploit C2 — Q3 |
| T1562.002 | Defense Evasion | Impair Defenses: Disable Windows Event Logging | Audit policy change — Q4 |
| T1053.005 | Persistence | Scheduled Task/Job: Scheduled Task | \HTB-AUTOMATION — Q5 |
| T1053 | Execution | Scheduled Task/Job | Scheduled task execution — Q5 |
| T1059.001 | Execution | Command and Scripting Interpreter: PowerShell | Get-FileHash via PowerShell — Q11 |
| T1074 | Collection | Data Staged | Hash computation of script — Q11 |
| T1069.002 | Discovery | Permission Groups Discovery: Domain Groups | SharpHound — Q8 |
| T1087.002 | Discovery | Account Discovery: Domain Account | SharpHound — Q8 |
| T1005 | Collection | Data from Local System | SharpHound enumeration — Q8 |
| T1070.001 | Defense Evasion | Indicator Removal: Clear Windows Event Logs | Firewall log cleared — Q12 |
10. Conclusions & Recommendations
10.1 Incident Summary
| What Happened | The user CyberJunkie logged in and performed a chain of malicious actions over ~25 minutes: downloaded SharpHound (quarantined), added a firewall rule for Metasploit C2 on port 4444, disabled audit logging, created a scheduled task for persistence, computed a hash of the script, and cleared the Firewall log. |
|---|---|
| Root Cause | A valid user account was used for malicious activity; no account lockout or MFA; Defender quarantined SharpHound but the attacker proceeded with other actions. |
| Impact Assessment | Confidentiality: High — SharpHound AD enumeration attempted. Integrity: High — firewall tampering, audit policy change, scheduled task persistence. Availability: Medium — targeted log clearing. |
10.2 Recommendations
| Priority | Timeframe | Recommendation |
|---|---|---|
| Immediate | Within 24h | Disable CyberJunkie account; remove \HTB-AUTOMATION task and Automation-HTB.ps1; block port 4444 outbound |
| High | Within 7 days | Restore Firewall log from backup; review all audit policy changes; check for additional persistence |
| Medium | Within 30 days | Alert on EID 4719 (audit policy change), EID 4698 (task creation by non-system), EID 2004 (firewall rule with port 4444), EID 104 (log clearing) |
| Low | Within 90 days | User awareness; restrict “Everyone” share permissions; implement MFA |
| Strategic | Ongoing | Baseline firewall rules and audit policies; monitor for SharpHound/BloodHound downloads |
11. Analyst Notes & Learning
11.1 What I Did Well
Correlated five different log sources (Security, Firewall, Defender, PowerShell, System) to reconstruct a 25-minute attack chain. Distinguished EventID 102 (log clearing, no details) from EventID 104 (log cleared with specific log name) to identify the targeted anti-forensics.
11.2 Key Takeaways
- Absent event logs ≠ absent evidence: even when logs are cleared, other sources (Defender, PowerShell, System) retain evidence.
- Targeted log clearing (only the Firewall log) is more suspicious than a blanket wipe — it indicates the attacker knew exactly what to hide.
- EventID 104 vs 102: 104 provides the specific log name; 102 does not. Always prefer 104 for attribution.
- SubcategoryGuid, not %% codes: for EID 4719, the SubcategoryGuid maps to the actual subcategory name.
- SharpHound quarantine didn’t stop the attacker — they pivoted to firewall tampering and persistence.
11.3 New Techniques
Multi-source log correlation (Security/Firewall/Defender/PowerShell/System), EventID 104 vs 102 distinction for log clearing, SubcategoryGuid mapping for audit policy changes, Hayabusa Defender Alert (High) rule for threat detection, and Splunk spath for JSON field extraction.
12. References
- LogJammer — Hack The Box Sherlock
- MITRE ATT&CK — T1562.004 Disable or Modify System Firewall
- MITRE ATT&CK — T1070.001 Clear Windows Event Logs
- MITRE ATT&CK — T1053.005 Scheduled Task
- chainsaw
- hayabusa
Walkthrough by Akenaton · HTB CDSA Portfolio · LogJammer Sherlock