Solved Trojan from Hack The Box!
| Field | Details |
|---|---|
| Case Reference | HTB-SHRLCK-TROJAN |
| Platform | Hack The Box — Sherlock |
| Category | Malware Analysis — Trojanized Software |
| Difficulty | — |
| Date Opened | 2023-05-30 |
| Severity | High |
| Status | Closed — training scenario |
| Host | DESKTOP-38NVPD0 · 192.168.116.133 |
| Memory Dump | memory capture/memory.vmem (Windows 10 build 19041) |
| Disk Artifact | disk_artifacts.ad1 |
| Network Capture | packet capture/network.pcapng |
1. Executive Summary
On 2023-05-30 a user named John on workstation DESKTOP-38NVPD0 (Windows 10 build 19041) downloaded Data_Recovery.zip from a free hosting site (praetorial-gears.000webhostapp.com). The ZIP contained Recovery_Setup.exe — a trojanized version of the legitimate FinalRecovery v3.0.7.0325 data recovery software, packaged as an Inno Setup installer. Upon execution the malware installed to C:\Program Files (x86)\FLSCover\Rec528\ and established C2 communication with multiple servers in the 45.12.253.x range via PHP endpoints (stuk.php, puk.php), which served additional binary payloads. The C2 infrastructure was confirmed via VirusTotal (4 of 8 contacted URLs flagged malicious).
This report reconstructs the intrusion using three evidence sources — memory (memory.vmem), disk (disk_artifacts.ad1) and network (network.pcapng) — analyzed with Volatility 3, Wireshark/tshark, PECmd, pyad1, exiftool, innoextract, Joe Sandbox and VirusTotal.
1.1 Incident Summary
| Field | Details |
|---|---|
| Incident Type | Trojanized software (FinalRecovery) with C2 payload delivery |
| Initial Access | User download of Data_Recovery.zip from a free hosting site |
| Discovery | Multi-source forensic triage (memory + disk + network) |
| First Execution | 2023-05-30 02:06:29 UTC (Prefetch) |
| Persistence | Inno Setup installer dropped to C:\Program Files (x86)\FLSCover\Rec528\ |
| Overall Severity | High |
1.2 Key Findings
- The lure was
Data_Recovery.ziphosted onpraetorial-gears.000webhostapp.com(000webhostapp, a free hosting platform). - The installer masqueraded as FinalRecovery v3.0.7.0325; the true product identity survived only in help/temp files.
Recovery_Setup.exe(SHA-256c34601c5…4b3193) was executed twice (run count 2).- The malware installed to
C:\Program Files (x86)\FLSCover\Rec528\and spawnedRec528.exeviais-NJBAT.tmp. - C2 communication to
45.12.253.72(stuk.php/puk.php) polled repeatedly;puk.phpserved a binary payload. - 4 of 8 contacted URLs were flagged malicious on VirusTotal; the rest were legitimate Sectigo/Microsoft certificate endpoints.
2. Investigation Scope & Artifacts
2.1 Artifacts Analyzed
| Artifact | Format | What it answers |
|---|---|---|
memory capture/memory.vmem |
Raw memory dump (Windows 10 build 19041) | OS info, hostname, process tree, command lines — Q1, Q2, Q5, Q6 |
disk_artifacts.ad1 |
AccessData AD1 image | Recovery_Setup.exe for hashing, Prefetch, Inno Setup temp files — Q7, Q8, Q9, Q10, Q13 |
packet capture/network.pcapng |
PCAP | Download URL, C2 communication — Q3, Q4, Q12 |
VirusTotal record for SHA-256 c34601c5…4b3193 |
Web | Contacted URLs, behavioral analysis — Q11, Q12 |
| Joe Sandbox report | Web | Impersonated product version (v3.0.7.0325) — Q13 |
2.2 Tools & Methods
| Tool | Purpose |
|---|---|
Volatility 3 (windows.info, windows.envars, windows.pslist, windows.pstree, windows.cmdline) |
Memory analysis |
| Wireshark / tshark | Network capture analysis |
| PECmd (Eric Zimmerman) | Prefetch parsing |
| pyad1 | AD1 image extraction on Linux |
| exiftool | PE metadata inspection |
| innoextract | Inno Setup installer extraction |
| Joe Sandbox | Behavioral analysis of the sample |
| VirusTotal | Hash reputation and contacted URLs |
3. Technical Analysis
3.1 Scenario
Multi-source forensic investigation of a trojanized FinalRecovery installer. Evidence spans memory (memory.vmem), disk (disk_artifacts.ad1) and network (network.pcapng). Objective: reconstruct the full intrusion — download, execution, C2 communication, payload delivery, and the impersonated software identity.
3.2 Q1 — What is the build version of the operating system?
Answer: 19041
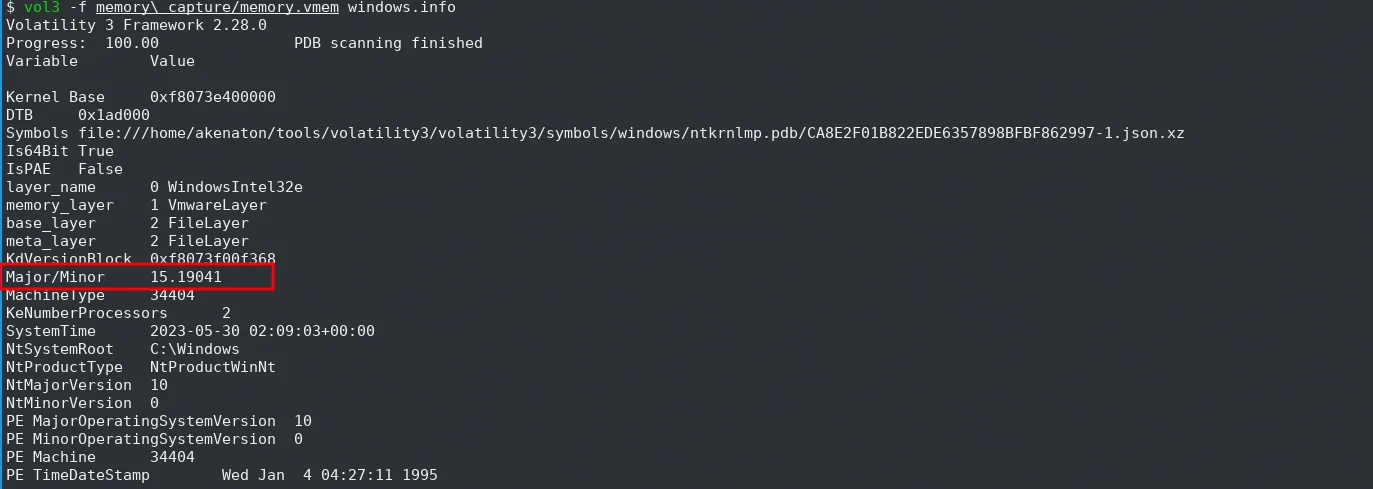
We used the windows.info plugin to retrieve system metadata from the memory dump:
$ vol3 -f memory\ capture/memory.vmem windows.info
Key indicators:
- The Major/Minor field shows 15.19041 — the minor version 19041 is the OS build number
- This corresponds to Windows 10 version 2004 (May 2020 Update), also known as 20H1
- Build 19041 is the base build for Windows 10 2004/20H1/20H2/21H1/21H2
- Additional useful info: 64-bit system, 2 processors, SystemTime 2023-05-30 02:09:03 UTC, system root at
C:\Windows
Detection angle. windows.info Major/Minor field reveals the OS build (19041) — anchors all subsequent timeline correlation.
3.3 Q2 — What is the computer hostname?
Answer: DESKTOP-38NVPD0
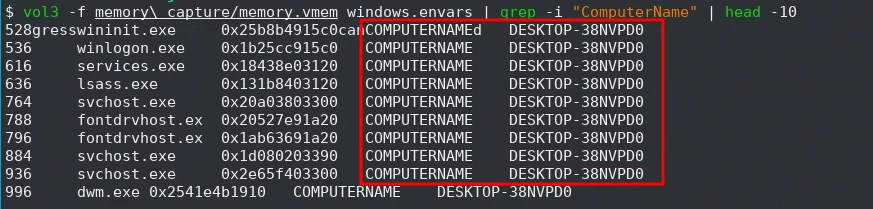
We used the windows.envars plugin to extract environment variables from all running processes and filtered for the COMPUTERNAME variable:
$ vol3 -f memory\ capture/memory.vmem windows.envars | grep -i "ComputerName" | head -10
Key indicators:
- The
COMPUTERNAMEenvironment variable consistently shows DESKTOP-38NVPD0 across all processes (smss, winlogon, services, lsass, svchost, etc.) - The
DESKTOP-XXXXXXXnaming convention is the default Windows 10 auto-generated hostname - This hostname is useful for correlating events across different evidence sources
Alternative approach: The hostname can also be retrieved from the registry in memory:
$ vol3 -f memory\ capture/memory.vmem windows.registry.printkey --key "ControlSet001\Control\ComputerName\ComputerName"
Detection angle. windows.envars filtered on COMPUTERNAME — hostname correlation across evidence sources.
3.4 Q3 — What is the name of the downloaded ZIP file?
Answer: Data_Recovery.zip
We analyzed the network capture using tshark, filtering HTTP requests containing .zip in the URI:
$ tshark -r packet\ capture/network.pcapng -Y "http.request.uri contains\".zip\"" -T fields -e frame.time -e ip.src -e ip.dst -e http.request.full_uri

The output reveals two HTTP requests for the same ZIP file:
- 2023-05-30 09:56:04 EEST —
192.168.116.133→145.14.144.155(initial GET request) - 2023-05-30 09:56:17 EEST —
145.14.144.155→192.168.116.133(follow-up request, likely a redirect or retry)
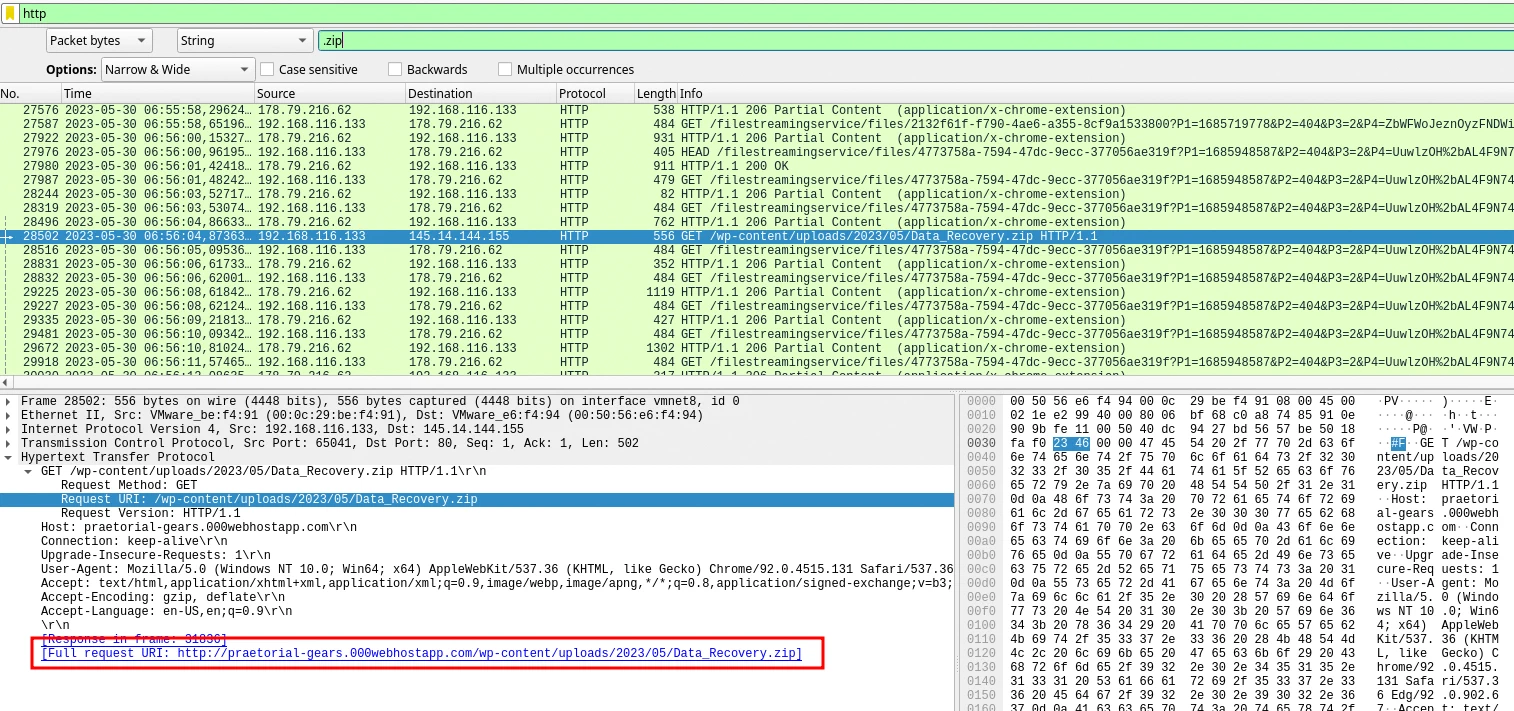
For deeper inspection, we examined the HTTP request in Wireshark with a display filter of http and searched packet bytes for the string .zip:
Key indicators:
- The full download URL is
http://praetorial-gears.000webhostapp.com/wp-content/uploads/2023/05/Data_Recovery.zip - The file is hosted on 000webhostapp.com — a free web hosting service commonly abused by threat actors
- The URL path contains
/wp-content/uploads/— indicating a WordPress site, possibly compromised - The User-Agent shows Chrome/92.0.4515.131 — the victim was using Google Chrome
- Source IP 192.168.116.133 is our victim machine; 145.14.144.155 is the hosting server
Detection angle. tshark HTTP filter for .zip URIs — identifies the downloaded lure and its hosting domain.
3.5 Q4 — What is the domain of the website (including the third-level domain) from which the file was downloaded?
Answer: praetorial-gears.000webhostapp.com
This was already identified in Q3 from the full request URI in the HTTP GET request:
http://praetorial-gears.000webhostapp.com/wp-content/uploads/2023/05/Data_Recovery.zip
Key indicators:
- Third-level domain (subdomain):
praetorial-gears— the attacker-controlled subdomain - Second-level domain:
000webhostapp.com— a free hosting platform by Hostinger, frequently abused for phishing and malware delivery - Free hosting services like this are attractive to threat actors because they require minimal identity verification
Detection angle. Free hosting domains (000webhostapp.com) serving executables/archives — proxy/DNS alerting on first-seen free-hosting domains.
3.6 Q5 — The user then executed the suspicious application found in the ZIP archive. What is the process PID?
Answer: 484
Since we know the downloaded file was Data_Recovery.zip, we searched for a process with a related name using windows.pslist:
$ vol3 -f memory\ capture/memory.vmem windows.pslist | grep -i "recovery" | column -t

Key indicators:
- PID 484 —
Recovery_Setupprocess, correlated with the downloadedData_Recovery.zip - The process was created at 2023-05-30 02:07:59 UTC
- PPID 60 — parent process ID (likely
explorer.exeif the user double-clicked it) - The naming convention
Recovery_SetupinsideData_Recovery.zipis a classic social engineering lure
We confirmed this with windows.pstree to see the full process hierarchy:
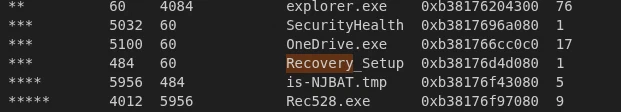
The process tree reveals:
- PID 60 (
explorer.exe, PPID 4084) → PID 484 (Recovery_Setup) — user double-clicked - PID 484 (
Recovery_Setup) → PID 5956 (is-NJBAT.tmp) → PID 4012 (Rec528.exe) — multi-stage payload
We also used windows.cmdline to confirm the full executable paths:

- PID 484:
"C:\Users\John\Downloads\Data_Recovery\Recovery_Setup.exe" - PID 5956:
"C:\Users\John\AppData\Local\Temp\is-VIBV9.tmp\is-NJBAT.tmp"
Detection angle. windows.pslist/pstree showing Recovery_Setup.exe spawning is-NJBAT.tmp → Rec528.exe — installer-based multi-stage payload.
3.7 Q6 — What is the full path of the suspicious process?
Answer: C:\Users\John\Downloads\Data_Recovery\Recovery_Setup.exe
This was already identified in Q5 using the windows.cmdline plugin, which revealed PID 484’s full executable path.
Detection angle. windows.cmdline full path confirms the drop location under the user’s Downloads folder.
3.8 Q7 — What is the SHA-256 hash of the suspicious executable?
Answer: c34601c5da3501f6ee0efce18de7e6145153ecfac2ce2019ec52e1535a4b3193
To get the correct hash, we needed the original on-disk file rather than a memory dump (dumping from memory produces files that may differ due to page alignment/relocation). We extracted the file from the disk artifact (disk_artifacts.ad1) using pyad1:
$ python3 extract_ad1.py "disk artifacts/disk_artifacts.ad1" "Recovery_Setup"
$ sha256sum exported_files/Recovery_Setup.exe

Key indicators:
- The SHA-256 hash uniquely identifies this malware sample
- This hash can be searched on threat intelligence platforms (VirusTotal, MalwareBazaar)
- Why not dump from memory?
windows.dumpfilesreconstructs files fromImageSectionObject/DataSectionObject, which may not be byte-identical to the on-disk binary
Note: When a question asks for a file hash, always prefer the disk artifact over memory dumps. Memory-reconstructed files are useful for behavioral analysis but unreliable for hash matching.
Detection angle. Disk-artifact hashing (pyad1) over memory dumping — reliable hash for threat intel lookup.
3.9 Q8 — When was the malicious program first executed?
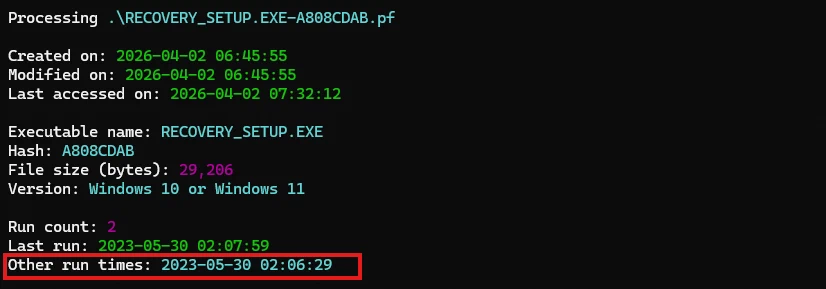
Answer: 2023-05-30 02:06:29
We extracted the Windows Prefetch file for Recovery_Setup.exe from the disk artifact and parsed it using PECmd:
$ PECmd.exe -f RECOVERY_SETUP.EXE-A808CDAB.pf
Key indicators:
- Run count: 2 — the executable was run twice
- Last run: 2023-05-30 02:07:59 — the second (most recent) execution (PID 484, Q5)
- Other run times: 2023-05-30 02:06:29 — the first execution
- The ~90-second gap suggests the user ran the installer once, then again (common when malware disguised as legitimate software shows no visible result)
Important distinction: Windows Prefetch tracks up to 8 historical timestamps. “Last run” is always the most recent, while “Other run times” contains previous executions in reverse chronological order. When investigating “first execution,” check the oldest entry in “Other run times.”
Detection angle. PECmd Prefetch parsing — distinguish “Last run” from “Other run times” for first-execution determination.
3.10 Q9 — How many times in total has the malicious application been executed?
Answer: 2
This was already identified in Q8 from the Prefetch analysis. The Run count: 2 field in the parsed RECOVERY_SETUP.EXE-A808CDAB.pf confirms exactly two executions:
- 2023-05-30 02:06:29 — first execution
- 2023-05-30 02:07:59 — second execution
Detection angle. Prefetch Run count field — confirms execution frequency.
3.11 Q10 — The malicious application references two .TMP files, one is IS-NJBAT.TMP, which is the other?
Answer: IS-R7RFP.TMP
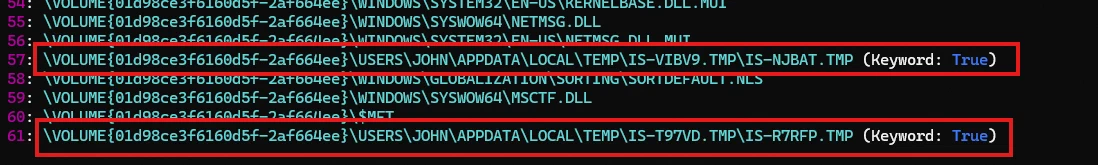
From the PECmd Prefetch analysis, we examined the Resources loaded section which lists all files referenced during execution:
Key indicators:
- Line 57:
\USERS\JOHN\APPDATA\LOCAL\TEMP\IS-VIBV9.TMP\IS-NJBAT.TMP(Keyword: True) - Line 61:
\USERS\JOHN\APPDATA\LOCAL\TEMP\IS-T97VD.TMP\IS-R7RFP.TMP(Keyword: True) - Both flagged with Keyword: True (matched PECmd’s keyword list for suspicious/notable references)
- The two
.TMPfiles reside in different parent temp directories — aligning with the two separate executions (Q8/Q9), as Inno Setup creates a unique temp directory per run - Characteristic of Inno Setup installer temporary files — the malware was packaged as a fake Inno Setup installer
Detection angle. Prefetch “Resources loaded” with Inno Setup temp files (IS-*.TMP) — installer-based staging.
3.12 Q11 — How many of the URLs contacted by the malicious application were detected as malicious by VirusTotal?
Answer: 4
We searched the SHA-256 hash from Q7 (c34601c5da…4b3193) on VirusTotal and examined the Relations tab under Contacted URLs:
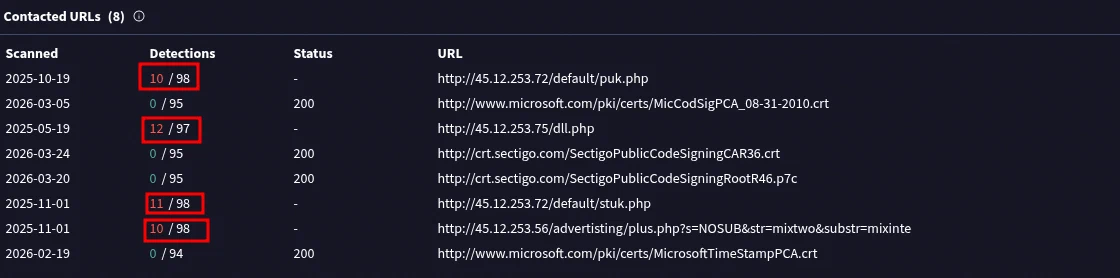
Out of 8 contacted URLs, 4 had detections (non-zero detection count):
| Detections | URL | Analysis |
|---|---|---|
| 10 / 98 | http://45.12.253.72/default/puk.php |
Malicious C2 endpoint |
| 12 / 97 | http://45.12.253.75/dll.php |
Malicious — likely serves a DLL payload |
| 11 / 98 | http://45.12.253.72/default/stuk.php |
Malicious C2 endpoint |
| 10 / 98 | http://45.12.253.56/advertising/plus.php?s=NOSUB&str=mixtwo&substr=mixinte |
Malicious C2 with parameters |
The remaining 4 URLs with 0 detections are legitimate:
microsoft.com— certificate downloads (code signing, timestamp)crt.sectigo.com— Sectigo CA certificate chain files
Key indicators:
- All malicious URLs point to bare IP addresses (
45.12.253.x) rather than domain names - The
.phpendpoints suggest a web-based C2 panel - The IPs are in the
45.12.253.0/24range — multiple C2 servers in the same subnet - The legitimate URLs are related to code signing certificates (Sectigo)
Detection angle. VirusTotal “Contacted URLs” tab — distinguishes malicious C2 (bare IPs, .php) from legitimate certificate endpoints.
3.13 Q12 — The malicious application downloaded a binary file from one of the C2 URLs, what is the name of the file?
Answer: puk.php
From the VirusTotal analysis in Q11, two PHP endpoints on the C2 server 45.12.253.72 stood out: puk.php and stuk.php. VirusTotal’s behavioral analysis indicated that puk.php served a binary download.
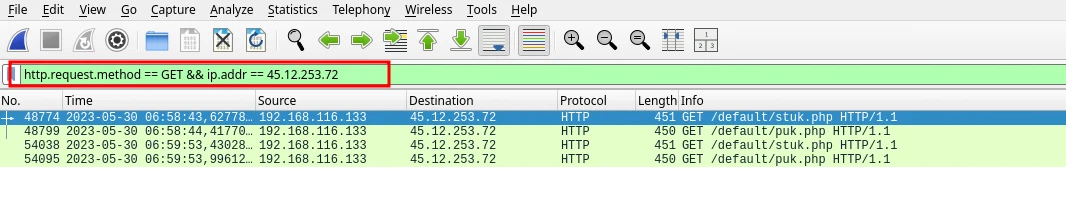
We confirmed the C2 communication in the network capture using Wireshark with the filter:
http.request.method == GET && ip.addr == 45.12.253.72
Key indicators:
- The victim machine (
192.168.116.133) made multiple HTTP GET requests to45.12.253.72:/default/stuk.php— at 06:58:43 and 06:59:53/default/puk.php— at 06:58:44 and 06:59:53
- The requests are paired and repeated, suggesting a polling pattern
puk.phpis the endpoint that served a binary payload;stuk.phplikely handles status/check-in- Both endpoints use the
/default/path prefix, consistent with a structured C2 web panel
Detection angle. Wireshark filter http.request.method == GET && ip.addr == 45.12.253.72 — paired stuk.php/puk.php polling pattern.
3.14 Q13 — Can you find any indication of the actual name and version of the program that the malware is pretending to be?
Answer: FinalRecovery v3.0.7.0325
This required multiple steps. First, we gathered clues from existing analysis:
- exiftool on
Recovery_Setup.exeshowed File Description: FLSCover and File Version: 1.0.5.28 — but this is the Inno Setup installer metadata, not the actual impersonated program - innoextract revealed the installer contained
finalrecovery.chm(a help file) andRec528.exe— hinting the program name is FinalRecovery - strings on the memory dump confirmed the installation path
C:\Program Files (x86)\FLSCover\Rec528\and references tofinalrecovery.chm
However, the exact version v3.0.7.0325 was not directly visible in memory strings or PE metadata. It was found by submitting the sample to Joe Sandbox, which revealed the content of a temporary file (is-AOCSC.tmp) dropped during installation:
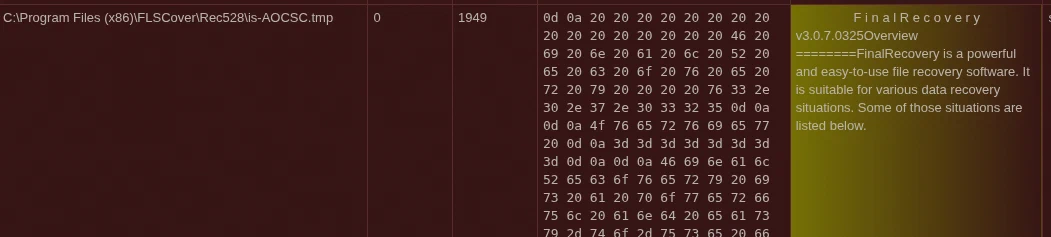
The file at C:\Program Files (x86)\FLSCover\Rec528\is-AOCSC.tmp contains:
FinalRecovery
v3.0.7.0325
Overview
========FinalRecovery is a powerful and easy-to-use file recovery software...
Key indicators:
- FinalRecovery is a legitimate data recovery application — the attacker trojanized it or repackaged it with malware
- The version v3.0.7.0325 is the version of the legitimate software being impersonated
- The installer brand name FLSCover and internal name Cov 1.0.5.28 appear to be the attacker’s modified metadata, while the original product identity was preserved in help/readme files
- This is a classic trojanized software technique — bundling malware with a legitimate application
Note: When identifying impersonated software, check temporary files, help files (.chm), readme files, and sandbox reports — the PE metadata is often modified by the attacker, but auxiliary files may retain the original product information.
Detection angle. Cross-reference PE metadata, innoextract output, memory strings and sandbox reports to recover the impersonated product identity.
4. Challenge Q&A Log
| # | Question | Answer | Method |
|---|---|---|---|
| 1 | OS build version | 19041 |
windows.info |
| 2 | Computer hostname | DESKTOP-38NVPD0 |
windows.envars |
| 3 | Downloaded ZIP file name | Data_Recovery.zip |
tshark HTTP filter |
| 4 | Download domain (with subdomain) | praetorial-gears.000webhostapp.com |
HTTP request URI |
| 5 | Suspicious process PID | 484 |
windows.pslist / pstree |
| 6 | Full path of suspicious process | C:\Users\John\Downloads\Data_Recovery\Recovery_Setup.exe |
windows.cmdline |
| 7 | SHA-256 of suspicious executable | c34601c5da3501f6ee0efce18de7e6145153ecfac2ce2019ec52e1535a4b3193 |
pyad1 extraction + sha256sum |
| 8 | First execution timestamp | 2023-05-30 02:06:29 |
PECmd Prefetch |
| 9 | Total execution count | 2 |
Prefetch Run count |
| 10 | Second .TMP file name | IS-R7RFP.TMP |
PECmd Resources loaded |
| 11 | Malicious contacted URLs count | 4 |
VirusTotal Relations tab |
| 12 | Binary-download C2 endpoint | puk.php |
VirusTotal + Wireshark |
| 13 | Impersonated program name/version | FinalRecovery v3.0.7.0325 |
innoextract + Joe Sandbox |
5. Incident Narrative
On 2023-05-30 user John on DESKTOP-38NVPD0 downloaded Data_Recovery.zip from praetorial-gears.000webhostapp.com (a free WordPress hosting site). The archive contained Recovery_Setup.exe — a trojanized Inno Setup installer impersonating FinalRecovery v3.0.7.0325. The victim executed it twice (02:06:29 and 02:07:59 UTC); the installer dropped to C:\Program Files (x86)\FLSCover\Rec528\ and spawned Rec528.exe through the Inno Setup temp file is-NJBAT.tmp.
The malware then established C2 communication with 45.12.253.72 over HTTP, polling stuk.php and puk.php in pairs; puk.php served a binary payload. VirusTotal showed 4 of 8 contacted URLs as malicious (all bare-IP 45.12.253.x endpoints); the remaining 4 were legitimate Sectigo/Microsoft certificate endpoints. The true product identity survived only in help/temp files (finalrecovery.chm, is-AOCSC.tmp), while the PE metadata was overwritten by the attacker (FLSCover / Cov 1.0.5.28).
6. Attack Timeline
| Timestamp (UTC) | Event | Artifact | ATT&CK |
|---|---|---|---|
| 2023-05-30 02:06:29 | First execution of Recovery_Setup.exe (trojanized installer) |
Prefetch (PECmd) | T1204.002 |
| 2023-05-30 02:06:48 | Rec528.exe (PID 3068) spawned — first payload run |
strings on memory dump |
T1059 |
| 2023-05-30 02:07:59 | Second execution of Recovery_Setup.exe (PID 484) |
windows.pslist, Prefetch |
T1204.002 |
| 2023-05-30 02:08:01 | Rec528.exe (PID 4012) spawned via is-NJBAT.tmp (PID 5956) |
windows.pstree |
T1059 |
| 2023-05-30 06:56:04 | Data_Recovery.zip downloaded from praetorial-gears.000webhostapp.com |
network.pcapng |
T1566.001 |
| 2023-05-30 06:58:43 | C2 communication begins — HTTP GET to 45.12.253.72 (stuk.php, puk.php) |
network.pcapng |
T1071.001 |
| 2023-05-30 06:58:44 | Binary payload downloaded from C2 via puk.php |
network.pcapng, VirusTotal |
T1105 |
Summary: User John on DESKTOP-38NVPD0 (Windows 10 build 19041) downloaded Data_Recovery.zip from a free hosting site. The ZIP contained Recovery_Setup.exe — a trojanized Inno Setup installer of FinalRecovery. Upon execution the malware installed to C:\Program Files (x86)\FLSCover\Rec528\ and established C2 communication with multiple servers in the 45.12.253.x range via PHP endpoints. The C2 infrastructure served additional binary payloads.
7. Indicators of Compromise (IOCs)
7.1 File IOCs
| Type | Value | Context |
|---|---|---|
| File Name | Data_Recovery.zip |
Downloaded lure — Q3 |
| File Name | Recovery_Setup.exe |
Trojanized installer — Q5/Q6 |
| File Name | Rec528.exe |
Embedded payload — timeline |
| File Name | is-NJBAT.tmp / IS-R7RFP.TMP |
Inno Setup temp files — Q10 |
| File Path | C:\Users\John\Downloads\Data_Recovery\ |
Drop location |
| File Path | C:\Program Files (x86)\FLSCover\Rec528\ |
Install location |
| File Path | C:\Users\John\AppData\Local\Temp\is-*\ |
Inno Setup staging |
| SHA-256 | c34601c5da3501f6ee0efce18de7e6145153ecfac2ce2019ec52e1535a4b3193 |
Recovery_Setup.exe — Q7 |
7.2 Network IOCs
| Type | Value | Context |
|---|---|---|
| Domain | praetorial-gears.000webhostapp.com |
Download host — Q4 |
| IP Address | 145.14.144.155 |
Hosting server — Q3 |
| IP Address | 45.12.253.72 |
C2 server (stuk.php, puk.php) — Q12 |
| IP Address | 45.12.253.75 |
C2 server (dll.php) — Q11 |
| IP Address | 45.12.253.56 |
C2 server (plus.php) — Q11 |
| IP Address | 192.168.116.133 |
Victim machine — Q3 |
| URL | http://45.12.253.72/default/stuk.php |
C2 check-in endpoint |
| URL | http://45.12.253.72/default/puk.php |
C2 payload endpoint |
| URL | http://45.12.253.75/dll.php |
C2 DLL endpoint |
| User-Agent | Chrome/92.0.4515.131 |
Download client — Q3 |
7.3 Behavioral IOCs
| Type | Value | Context |
|---|---|---|
| Process | Recovery_Setup.exe → is-NJBAT.tmp → Rec528.exe |
Multi-stage execution chain — Q5 |
| Registry/PE metadata | File Description FLSCover, File Version 1.0.5.28 |
Attacker-overwritten metadata — Q13 |
| Pattern | Bare-IP C2 URLs (no domain names) | Evasion of DNS-based detection — Q11 |
8. Detection Opportunities
| Source | What to look for | Why it matters |
|---|---|---|
| Network (PCAP/proxy) | Downloads of .zip from free hosting (000webhostapp.com) |
Initial access lure — Q3/Q4 |
Volatility windows.pslist/pstree |
Recovery_Setup.exe spawning is-*.tmp → Rec528.exe |
Installer-based multi-stage payload — Q5 |
Volatility windows.cmdline |
Full path under C:\Users\…\Downloads\ |
Confirms drop location — Q6 |
| Disk (Prefetch) | RECOVERY_SETUP.EXE-*.pf with Run count and temp file references |
Execution count and staging — Q8/Q10 |
| Network (PCAP) | HTTP GET to bare IPs 45.12.253.x with .php endpoints |
C2 communication — Q12 |
| VirusTotal | Hash lookup of unknown installer executables | Contacted URLs and detections — Q11 |
| PE metadata | File Description/Version mismatch with claimed product | Trojanized software detection — Q13 |
9. MITRE ATT&CK Mapping
| TTP ID | Tactic | Technique | Evidence |
|---|---|---|---|
| T1566.001 | Initial Access | Phishing: Spearphishing Attachment | Data_Recovery.zip downloaded from free hosting — Q3/Q4 |
| T1204.002 | Execution | User Execution: Malicious File | Recovery_Setup.exe executed twice — Q8/Q9 |
| T1059 | Execution | Command and Scripting Interpreter | Inno Setup temp file execution — Q5 |
| T1071.001 | Command and Control | Application Layer Protocol: Web Protocols | HTTP C2 to 45.12.253.72 — Q12 |
| T1105 | Command and Control | Ingress Tool Transfer | Binary payload via puk.php — Q12 |
| T1036 | Defense Evasion | Masquerading | PE metadata overwritten (FLSCover); FinalRecovery impersonation — Q13 |
10. Conclusions & Recommendations
10.1 Incident Summary
| What Happened | A user downloaded and executed a trojanized FinalRecovery installer; the malware installed to FLSCover\Rec528\, spawned a secondary payload, and established C2 communication with multiple 45.12.253.x servers serving binary payloads. |
|---|---|
| Root Cause | Social engineering lure (data-recovery utility) hosted on a free hosting platform; no application control or reputation check intercepted the download/execution. |
| Impact Assessment | Confidentiality: High — C2 payload delivery and potential data access. Integrity: High — unauthorized software installed. Availability: Medium — trojanized installer may disrupt legitimate recovery workflows. |
10.2 Recommendations
| Priority | Timeframe | Recommendation |
|---|---|---|
| Immediate | Within 24h | Block praetorial-gears.000webhostapp.com and 45.12.253.0/24 at DNS/proxy/firewall; hunt c34601c5…4b3193 and Rec528.exe estate-wide |
| High | Within 7 days | Remove FLSCover\Rec528\ from affected hosts; check for persistence mechanisms |
| Medium | Within 30 days | Alert on Inno Setup temp files (is-*.tmp) spawning executables; alert on HTTP to bare-IP .php endpoints |
| Low | Within 90 days | Application control (allow-list) for installers; phishing awareness for “data recovery” lures |
| Strategic | Ongoing | Multi-source forensics (memory + disk + network) as standard triage; document pyad1/PECmd workflow |
11. Analyst Notes & Learning
11.1 What I Did Well
Cross-correlated three evidence sources (memory, disk, network) and verified the hash from the disk artifact (pyad1) rather than from memory (which would have produced a wrong hash). Used VirusTotal in query-only mode for reputation and contacted URLs.
11.2 Key Takeaways
- Memory dumps are not byte-identical to disk files:
windows.dumpfilesproduces page-aligned reconstructions — use disk artifacts for hashes. - Prefetch keeps up to 8 timestamps: distinguish “Last run” from “Other run times” for first-execution questions.
- Free hosting (000webhostapp.com) is a common malware delivery channel.
- Trojanized software hides its identity in auxiliary files: help files (
.chm), temp files (is-*.tmp) and sandbox reports retain the original product name even when PE metadata is overwritten. - Bare-IP C2 URLs (no domain names) evade DNS-based detection.
11.3 New Techniques
pyad1 for AD1 extraction on Linux, PECmd Prefetch parsing, innoextract for Inno Setup installers, exiftool PE metadata inspection, Joe Sandbox for behavioral analysis, multi-source correlation (memory + disk + network), and VirusTotal Relations tab for contacted-URL reputation.
12. References
- Trojan — Hack The Box Sherlock
- MITRE ATT&CK — T1204.002 User Execution
- MITRE ATT&CK — T1071.001 Web Protocols
- pyad1 — AD1 reader for Python
- PECmd — Prefetch parser
- innoextract
HTB Sherlock · Trojan · Malware Analysis · 2023-05-30