Solved Vantage from Hack The Box!
| Field | Details |
|---|---|
| Case Reference | HTB-SHRLCK-VANTAGE |
| Platform | Hack The Box — Sherlock |
| Category | Network Analysis — Cloud Breach (OpenStack) |
| Difficulty | — |
| Date Opened | 2026-01-07 |
| Severity | High |
| Status | Closed — training scenario |
| Hosts | controller, web-server (pcap files) |
| Stack | Suricata, Zeek, Wireshark, tshark |
| Attacker IP | 117.200.21.26 |
Scenario: A small company moved some of its resources to a private cloud installation. The developers left the redirect to the dashboard on their web server. The security team got an email from the alleged attacker stating that the user data was leaked. It is up to you to investigate the situation.
1. Executive Summary
On 2025-07-01 an attacker at 117.200.21.26 fuzzed the company’s web server with ffuf v2.1.0, discovering the subdomain cloud.vantage.tech. After 3 login attempts, the attacker authenticated to the OpenStack dashboard, downloaded the admin-openrc.sh API credentials file (09:40:29 UTC), and transitioned to direct API access (09:41:44 UTC). They enumerated the Swift object store, discovered 3 containers (dev-files, employee-data, user-data), exfiltrated user-data (28 user records, 09:45:23 UTC) and employee-data, then created a backdoor admin user jellibean (password P@$$word) for persistence. The entire intrusion — from fuzzing to data exfiltration to backdoor creation — was reconstructed from two PCAPs (web-server.pcap, controller.pcap) using tshark, Zeek and Wireshark.
1.1 Incident Summary
| Field | Details |
|---|---|
| Incident Type | Cloud breach — OpenStack dashboard fuzzing → credential theft → data exfiltration → backdoor user |
| Initial Access | Fuzzing the web server with ffuf, discovering cloud.vantage.tech |
| Discovery | Security team received an email from the alleged attacker |
| First Interaction | 2025-07-01 (fuzzing observed in PCAP) |
| Persistence | Backdoor admin user jellibean (password P@$$word) |
| Overall Severity | High |
1.2 Key Findings
- Fuzzing tool: ffuf v2.1.0 (User-Agent “Fuzz Faster U Fool v2.1.0-dev”), 3,695 requests from
117.200.21.26. - Discovered subdomain:
cloud.vantage.tech(21 requests vs. 2 for others). - 3 login attempts before successful dashboard authentication.
admin-openrc.shdownloaded at 09:40:29 UTC — OpenStack API credentials (endpoint, project ID, username, password).- First API interaction at 09:41:44 UTC (compute/nova GET).
- Default project ID:
9fb84977ff7c4a0baf0d5dbb57e235c7. - Authentication service: Keystone; object storage (Swift) endpoint:
http://134.209.71.220:8080/v1/AUTH_9fb84977…. - 3 containers discovered:
dev-files,employee-data,user-data. user-dataexfiltrated at 09:45:23 UTC — 28 user records.- Backdoor admin user
jellibeancreated with passwordP@$$word(plaintext in HTTP, no TLS).
2. Investigation Scope & Artifacts
2.1 Artifacts Analyzed
| Artifact | Format | What it answers |
|---|---|---|
web-server.2025-07-01.pcap |
PCAP | Fuzzing, login attempts, subdomain discovery — Q1, Q2, Q3 |
controller.pcap |
PCAP | OpenStack API interactions, Swift exfiltration, user creation — Q4–Q13 |
| Zeek/Zui logs | JSON | HTTP method/URI filtering — Q4, Q5, Q6, Q10 |
2.2 Tools & Methods
| Tool | Purpose |
|---|---|
| tshark | Packet capture analysis (HTTP filtering, field extraction) |
| Wireshark | Visual inspection of HTTP requests |
| Zeek / Zui | HTTP log querying (_path=="http") |
jq |
JSON parsing of exported Swift container data |
3. Technical Analysis
3.1 Scenario
Network pcap analysis of a cloud breach. A small company moved resources to a private OpenStack cloud. Developers left a redirect to the dashboard on their web server. The security team received an email from the alleged attacker stating user data was leaked. Investigate the situation.
3.2 Q1 — What tool did the attacker use to fuzz the web server? (Format: include version)
Answer: ffuf@2.1.0
tshark -r web-server.2025-07-01.pcap -Y "http.request" -T fields -e ip.src -e ip.dst | uniq -c | sort -un
   1 10.116.0.3      10.116.0.4
   2 184.105.247.252 157.230.81.229
 302 117.200.21.26   157.230.81.229
3394 117.200.21.26   157.230.81.229
tshark -r web-server.2025-07-01.pcap -Y "http.request" -T fields -e ip.src -e ip.dst -e http.user_agent | sort | uniq -c | sort -un
      1 10.116.0.3      10.116.0.4      Fuzz Faster U Fool v2.1.0-dev
      2 184.105.247.252 157.230.81.229  Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 …
     20 10.116.0.3      10.116.0.4      Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) …
   3695 117.200.21.26   157.230.81.229  Fuzz Faster U Fool v2.1.0-dev
Notes: At first I ran tshark filtering http.request communications on the pcap. We saw 3394 http.requests from SourceIP 117.200.21.26 to 157.230.81.229 — probably fuzzing. On the second tshark command (with User-Agent), we found Fuzz Faster U Fool v2.1.0-dev — the answer is ffuf@2.1.0.
Detection angle. tshark HTTP request aggregation by ip.src/ip.dst/http.user_agent — reveals fuzzing tool and attacker IP.
3.3 Q2 — Which subdomain did the attacker discover?
Answer: cloud
tshark -r web-server.2025-07-01.pcap -Y "http and ip.src==117.200.21.26" -T fields -e http.host | sort | uniq -c | sort -n
      2 www3.vantage.tech
      2 www.blog.vantage.tech
      2 www.dev.vantage.tech
      2 www.forum.vantage.tech
      2 www.m.vantage.tech
      2 www.test.vantage.tech
      2 www.vantage.tech
     21 cloud.vantage.tech
Notes: Filtered http and ip.src and extracted -e http.host. cloud.vantage.tech has more occurrences (21 vs 2), so the answer is cloud.
Detection angle. tshark http.host aggregation — subdomain with disproportionate request count reveals the discovered endpoint.
3.4 Q3 — How many login attempts did the attacker make before successfully logging in to the dashboard?
Answer: 3
Wireshark display filter:
http && ip.addr == 117.200.21.26 && http.referer == http://cloud.vantage.tech/dashboard/auth/login/
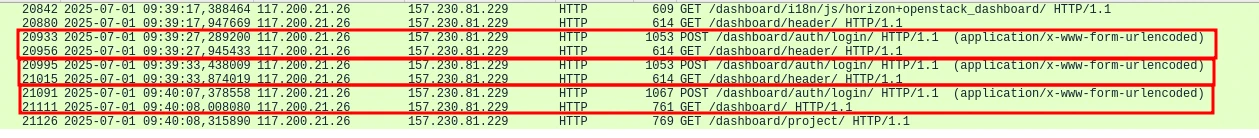
Notes: 3 login attempts observed. The 3rd succeeded because we saw /dashboard/project/ afterwards.
Detection angle. Wireshark filter on http.referer to the login endpoint — counts failed vs. successful login attempts.
3.5 Q4 — When did the attacker download the OpenStack API remote access config file? (UTC)
Answer: 2025-07-01 09:40:29
Zeek query:
_path=="http" | id.orig_h==117.200.21.26 | cut ts, uid, method, uri, referrer, resp_filenames

Notes: Using Zeek/Zui HTTP logs, filtered by attacker IP 117.200.21.26 and inspected the resp_filenames field. At 2025-07-01 09:40:29 UTC the attacker downloaded admin-openrc.sh from /dashboard/project/api_access/openrc/. admin-openrc.sh is an OpenStack credentials file containing API endpoint URLs, project ID, username, and password. Possession of this file gives the attacker full programmatic access to the OpenStack cloud infrastructure via CLI or API, bypassing the web dashboard entirely.
Detection angle. Zeek HTTP logs with resp_filenames — identifies credential file download.
3.6 Q5 — When did the attacker first interact with the API on controller node? (UTC)
Answer: 2025-07-01 09:41:44
_path=="http" | cut ts, method, uri
Notes: After downloading admin-openrc.sh at 09:40:29, the attacker used the credentials to authenticate directly against the OpenStack API. At 2025-07-01 09:41:44 UTC the first API interaction was observed — a GET request to the compute/nova API endpoint, approximately 75 seconds after the openrc file was downloaded. This confirms the attacker transitioned from web dashboard browsing to direct API access using the stolen credentials — a significant escalation giving programmatic control over the cloud infrastructure.
Detection angle. Zeek HTTP logs — first API request after credential file download indicates API access transition.
3.7 Q6 — What is the project id of the default project accessed by the attacker?
Answer: 9fb84977ff7c4a0baf0d5dbb57e235c7
_path=="http" | id.orig_h==117.200.21.26 | cut ts, uid, method, host, uri | projects
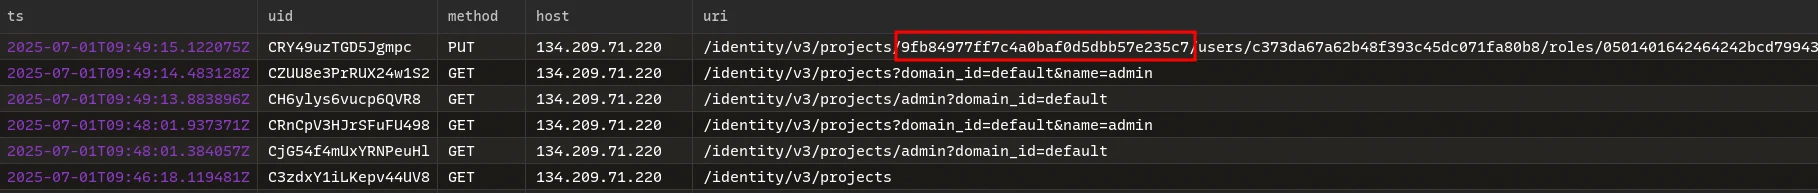
Notes: At 09:48:01 UTC the attacker queried the Identity API: GET /identity/v3/projects?domain_id=default&name=admin. The project ID 9fb84977ff7c4a0baf0d5dbb57e235c7 was returned and confirmed visible in the PUT request at 09:49:15 UTC where the attacker used it to assign the admin role to the backdoor account jellibean.
Detection angle. Zeek HTTP logs — Identity API project enumeration reveals the default project ID.
3.8 Q7 — Which OpenStack service provides authentication and authorization for the OpenStack API?
Answer: keystone
Notes: According to documentation, Keystone is an OpenStack service that provides API client authentication, service discovery, and distributed multi-tenant authorization by implementing OpenStack’s Identity API.
Detection angle. Keystone = OpenStack Identity service — all auth flows go through it.
3.9 Q8 — What is the endpoint URL of the swift service?
Answer: http://134.209.71.220:8080/v1/AUTH_9fb84977ff7c4a0baf0d5dbb57e235c7
Notes: Swift endpoint URL found by filtering port 8080 traffic in Zui. All object storage requests used host 134.209.71.220:8080 with path /v1/AUTH_[project_id], confirming the full endpoint URL: http://134.209.71.220:8080/v1/AUTH_9fb84977ff7c4a0baf0d5dbb57e235c7.
Detection angle. Port 8080 traffic to 134.209.71.220 — Swift object storage endpoint.
3.10 Q9 — How many containers were discovered by the attacker?
Answer: 3 — dev-files, employee-data, user-data
tshark -r controller.pcap --export-objects http,./extracted/
cat ./extracted/AUTH_9fb84977ff7c4a0baf0d5dbb57e235c7%3fformat=json | jq .
[
  { "name": "dev-files", "count": 0, "bytes": 0, "last_modified": "2025-07-01T04:22:36.008860", "storage_policy": "Policy-0" },
  { "name": "employee-data", "count": 0, "bytes": 0, "last_modified": "2025-07-01T04:22:28.334080", "storage_policy": "Policy-0" },
  { "name": "user-data", "count": 0, "bytes": 0, "last_modified": "2025-07-01T04:22:07.707130", "storage_policy": "Policy-0" }
]

Notes: At 09:43:27 UTC the attacker queried the Swift storage root: GET /v1/AUTH_9fb84977ff7c4a0baf0d5dbb57e235c7?format=json. The 376-byte JSON response revealed 3 containers: dev-files (empty, never accessed), employee-data (exfiltrated at 09:45:47 UTC), user-data (exfiltrated at 09:45:23 UTC).
Detection angle. Swift ?format=json container listing — reveals all storage containers.
3.11 Q10 — When did the attacker download the sensitive user data file? (UTC)
Answer: 2025-07-01 09:45:23
_path=="http"
| id.orig_h == 117.200.21.26
| "user-data"
| cut ts, method, id.orig_h, uri, response_body_len
| sort ts

Notes: Filtered HTTP traffic from attacker IP 117.200.21.26 for all requests targeting the user-data container. The download was identified by the GET request with a non-zero response body.
Detection angle. Zeek HTTP logs filtered by id.orig_h and container name — identifies the exfiltration timestamp.
3.12 Q11 — How many user records are in the sensitive user data file?
Answer: 28
cat user-details.csv | wc -l  → 29 lines
29 - 1 (header) = 28 user records
Notes: Exported user-details.csv from the PCAP using Wireshark. Counted rows excluding the header line.
Detection angle. Exported CSV row count (minus header) — quantifies exfiltration scope.
3.13 Q12 — For persistence, the attacker created a new user with admin privileges. What is the username of the new user?
Answer: jellibean
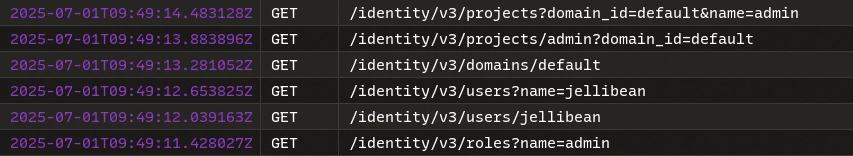
$ grep -r "jellibean"
users(1):{"user": {"password": "P@$$word", "enabled": true, "default_project_id": "9fb84977ff7c4a0baf0d5dbb57e235c7", "name": "jellibean"}}
users(2):{"user": {"id": "c373da67a62b48f393c45dc071fa80b8", "name": "jellibean", "domain_id": "default", "enabled": true, "default_project_id": "9fb84977ff7c4a0baf0d5dbb57e235c7", "password_expires_at": null, "options": {}, "links": {"self": "http://134.209.71.220/identity/v3/users/c373da67a62b48f393c45dc071fa80b8"}}}
Notes: Ran grep -r "jellibean" against all HTTP objects extracted from controller.pcap. Found the user creation POST request body confirming username jellibean with default_project_id matching the admin project.
Detection angle. grep on extracted HTTP objects for the backdoor username — confirms user creation.
3.14 Q13 — What is the password of the new user?
Answer: P@$$word
Notes: Password found in the same POST /identity/v3/users request body extracted in Q12. Plaintext credentials in API traffic confirm no encryption was used on the internal network (HTTP not HTTPS).
Detection angle. Plaintext password in HTTP POST body — credential exposure in unencrypted API traffic.
4. Challenge Q&A Log
| # | Question | Answer | Method |
|---|---|---|---|
| 1 | Fuzzing tool used | ffuf@2.1.0 |
tshark User-Agent |
| 2 | Subdomain discovered | cloud |
tshark http.host aggregation |
| 3 | Login attempts before success | 3 |
Wireshark filter on login referer |
| 4 | OpenStack API config download time | 2025-07-01 09:40:29 |
Zeek HTTP logs (resp_filenames) |
| 5 | First API interaction time | 2025-07-01 09:41:44 |
Zeek HTTP logs |
| 6 | Default project ID | 9fb84977ff7c4a0baf0d5dbb57e235c7 |
Zeek Identity API query |
| 7 | Authentication/authorization service | keystone |
OpenStack documentation |
| 8 | Swift service endpoint URL | http://134.209.71.220:8080/v1/AUTH_9fb84977… |
Port 8080 traffic in Zui |
| 9 | Containers discovered | 3 (dev-files, employee-data, user-data) |
Swift ?format=json response |
| 10 | User data file download time | 2025-07-01 09:45:23 |
Zeek HTTP logs filtered by container |
| 11 | User records in sensitive file | 28 |
CSV row count (minus header) |
| 12 | Backdoor admin username | jellibean |
grep on extracted HTTP objects |
| 13 | Backdoor admin password | P@$$word |
POST body in extracted HTTP objects |
5. Incident Narrative
On 2025-07-01 an attacker at 117.200.21.26 fuzzed the company’s web server with ffuf v2.1.0 (3,695 requests), discovering the subdomain cloud.vantage.tech. After 3 login attempts, the attacker authenticated to the OpenStack dashboard, downloaded the admin-openrc.sh API credentials file (09:40:29 UTC), and transitioned to direct API access (09:41:44 UTC). They enumerated the Swift object store, discovered 3 containers (dev-files, employee-data, user-data), exfiltrated user-data (28 user records, 09:45:23 UTC) and employee-data, then created a backdoor admin user jellibean (password P@$$word) for persistence. The entire intrusion — from fuzzing to data exfiltration to backdoor creation — was reconstructed from two PCAPs using tshark, Zeek and Wireshark.
6. Attack Timeline
| Timestamp (UTC) | Event | Artifact | ATT&CK |
|---|---|---|---|
| (fuzzing phase) | ffuf v2.1.0 fuzzing from 117.200.21.26 (3,695 requests) |
web-server.pcap |
T1595.002 |
| (discovery) | Subdomain cloud.vantage.tech discovered (21 requests) |
web-server.pcap |
T1595.002 |
| (auth phase) | 3 login attempts; 3rd successful | web-server.pcap |
T1110 |
| 09:40:29 | admin-openrc.sh downloaded (API credentials) |
Zeek HTTP logs | T1552.005 |
| 09:41:44 | First API interaction on controller node (compute/nova) | Zeek HTTP logs | T1078 |
| 09:43:27 | Swift container listing (3 containers) | Zeek HTTP logs | T1530 |
| 09:45:23 | user-data container exfiltrated (28 records) |
Zeek HTTP logs | T1530 |
| 09:45:47 | employee-data container exfiltrated |
Zeek HTTP logs | T1530 |
| (persistence) | Backdoor user jellibean created (password P@$$word) |
controller.pcap |
T1136.003 |
7. Indicators of Compromise (IOCs)
7.1 File IOCs
| Type | Value | Context |
|---|---|---|
| File Name | admin-openrc.sh |
OpenStack API credentials file — Q4 |
| File Name | user-details.csv |
Exfiltrated user data (28 records) — Q11 |
7.2 Network IOCs
| Type | Value | Context |
|---|---|---|
| IP Address | 117.200.21.26 |
Attacker IP — Q1 |
| IP Address | 157.230.81.229 |
Web server — Q1 |
| IP Address | 134.209.71.220 |
OpenStack controller (Swift endpoint) — Q8 |
| Domain | cloud.vantage.tech |
Discovered subdomain (OpenStack dashboard) — Q2 |
| Domain | vantage.tech |
Company domain |
| Port | 8080 |
Swift object storage endpoint — Q8 |
| User-Agent | Fuzz Faster U Fool v2.1.0-dev |
ffuf v2.1.0 — Q1 |
7.3 Behavioral IOCs
| Type | Value | Context |
|---|---|---|
| Account | jellibean |
Backdoor admin user (password P@$$word) — Q12/Q13 |
| Account | admin |
Compromised OpenStack admin account |
| Project ID | 9fb84977ff7c4a0baf0d5dbb57e235c7 |
Default admin project — Q6 |
| Container | user-data, employee-data, dev-files |
Swift containers — Q9 |
| Credential | admin-openrc.sh (plaintext API creds) |
Stolen OpenStack credentials — Q4 |
| Protocol | HTTP (no TLS) | Plaintext credentials in API traffic — Q13 |
8. Detection Opportunities
| Source | What to look for | Why it matters |
|---|---|---|
| Network (PCAP/proxy) | High volume of HTTP requests from a single IP with Fuzz Faster U Fool User-Agent |
ffuf web fuzzing — Q1 |
| Network (DNS/proxy) | Requests to cloud.vantage.tech from unusual IPs |
Subdomain discovery — Q2 |
| Network (PCAP) | 3+ failed login attempts to a dashboard followed by success | Credential guessing — Q3 |
| Network (PCAP/Zeek) | Download of admin-openrc.sh or *openrc.sh files |
OpenStack credential theft — Q4 |
| Network (PCAP/Zeek) | HTTP requests to /identity/v3/ and /v1/AUTH_* from new IPs |
Direct API access with stolen creds — Q5/Q6 |
| Network (PCAP) | Swift ?format=json container listing followed by bulk GETs |
Data exfiltration — Q9/Q10 |
| Network (PCAP) | POST to /identity/v3/users creating a new admin user |
Backdoor account creation — Q12 |
| Network (PCAP) | Plaintext passwords in HTTP POST bodies | Credential exposure (no TLS) — Q13 |
9. MITRE ATT&CK Mapping
| TTP ID | Tactic | Technique | Evidence |
|---|---|---|---|
| T1595.002 | Reconnaissance | Active Scanning: Vulnerability Scanning | ffuf fuzzing of the web server — Q1/Q2 |
| T1110 | Credential Access | Brute Force | 3 login attempts before success — Q3 |
| T1552.005 | Credential Access | Unsecured Credentials: Cloud Instance Metadata API | admin-openrc.sh downloaded (API creds) — Q4 |
| T1078 | Defense Evasion | Valid Accounts | Authenticated to OpenStack with stolen creds — Q5 |
| T1530 | Collection | Data from Cloud Storage | Swift container enumeration and exfiltration — Q9/Q10 |
| T1136.003 | Persistence | Create Account: Cloud Account | Backdoor user jellibean created — Q12 |
| T1048 | Exfiltration | Exfiltration Over Alternative Protocol | Data exfiltrated over HTTP (no TLS) — Q10/Q13 |
10. Conclusions & Recommendations
10.1 Incident Summary
| What Happened | An attacker fuzzed the web server, discovered the OpenStack dashboard, stole API credentials, exfiltrated user data (28 records) from Swift storage, and created a backdoor admin account — all over unencrypted HTTP. |
|---|---|
| Root Cause | Developers left a redirect to the dashboard on the web server; OpenStack API credentials were downloadable via the web UI; internal API traffic was unencrypted (HTTP not HTTPS). |
| Impact Assessment | Confidentiality: Critical — 28 user records + employee data exfiltrated. Integrity: High — backdoor admin account created. Availability: Low — no service disruption observed. |
10.2 Recommendations
| Priority | Timeframe | Recommendation |
|---|---|---|
| Immediate | Within 24h | Disable jellibean account; revoke admin-openrc.sh credentials; block 117.200.21.26 at the WAF/firewall |
| High | Within 7 days | Enable HTTPS/TLS on all OpenStack API endpoints; remove the dashboard redirect from the web server |
| Medium | Within 30 days | Alert on ffuf User-Agent or high-volume 404s from single IPs; alert on admin-openrc.sh downloads; alert on new admin user creation |
| Low | Within 90 days | Implement rate limiting on the dashboard login; MFA for OpenStack admin accounts |
| Strategic | Ongoing | Network segmentation for cloud management plane; encrypt all internal API traffic; least-privilege for Swift containers |
11. Analyst Notes & Learning
11.1 What I Did Well
Correlated two PCAPs (web-server + controller) to reconstruct the full kill chain: fuzzing → login → credential theft → API access → container enumeration → exfiltration → backdoor. Used Zeek/Zui HTTP logs for efficient filtering by id.orig_h and URI patterns.
11.2 Key Takeaways
- ffuf’s User-Agent (“Fuzz Faster U Fool”) is a dead giveaway — trivial to detect in proxy/WAF logs.
admin-openrc.shis a credential goldmine — it contains the full OpenStack auth bundle (endpoint, project ID, username, password).- OpenStack API access over HTTP exposes credentials and data in plaintext — always use HTTPS.
- Swift container listing (
?format=json) reveals all storage containers in one request. - Backdoor accounts (
jellibean) with plaintext passwords in HTTP POST bodies are easy to spot in PCAPs. - Double-extension and masquerading apply to cloud too —
cloud.vantage.techwas the hidden entry point.
11.3 New Techniques
tshark HTTP aggregation by ip.src/http.user_agent, Zeek/Zui HTTP log querying (_path=="http", id.orig_h, resp_filenames), Wireshark display filters for login referers, tshark --export-objects http for file extraction, and grep -r on extracted HTTP objects for credential recovery.
12. References
- Vantage — Hack The Box Sherlock
- MITRE ATT&CK — T1595.002 Vulnerability Scanning
- MITRE ATT&CK — T1552.005 Cloud Instance Metadata API
- MITRE ATT&CK — T1530 Data from Cloud Storage
- MITRE ATT&CK — T1136.003 Create Account: Cloud Account
- OpenStack Keystone Documentation
- OpenStack Swift Documentation
- ffuf — Fuzz Faster U Fool
- Zeek
HTB Sherlock · Vantage · Network Analysis · 2026-01-07